OSPF Down Bit Loop Prevention Explained with MPLS L3VPN
Table of Contents
- What is the OSPF Down bit? ‹
- OSPF Down bit with MPLS L3VPN dual PE routers ‹
- Packet capture OSPF Down bit ‹
- Download section ‹
What is the OSPF Down bit?
A Provider Edge (PE) router in an MPLS L3VPN sets the OSPF Down bit for prefixes advertised to a Customer Edge (CE) router. In case a CE is connected to two PE routers, a routing loop may occur by redistributing OSPF prefixes into the MPLS backbone more than once. The OSPF Down bit (DN) protects against these kind of loops.
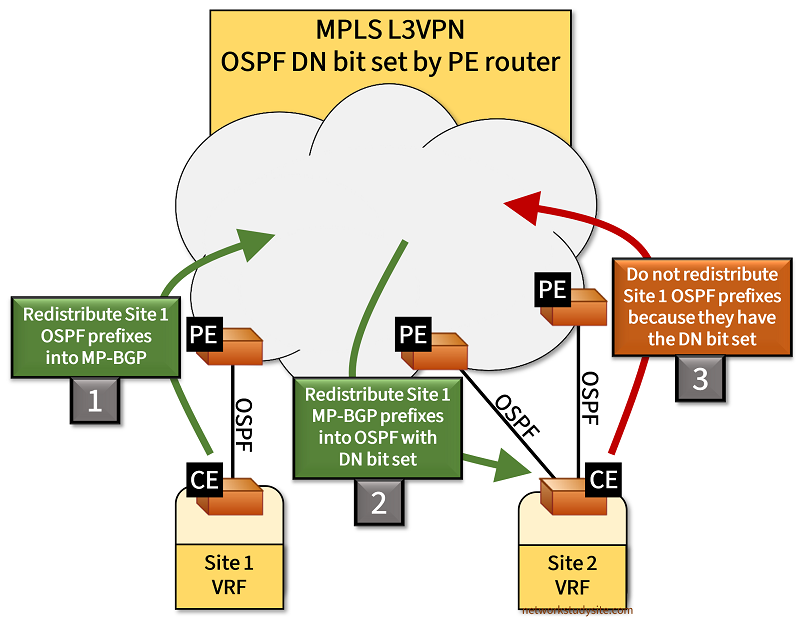
The above image focuses on the importance of the OSPF DN bit in a dual PE redundant MPLS VPN connection. As visible, the Site 2 CE router is connected to two PE routers which advertise Site 1 prefixes with the DN bit set. In turn, when the Site 2 CE router receives a Site 1 prefix advertisement via OSPF, it actually forwards the LSA to the other directly connected PE router. The DN bit stops the dual PE routers from redistributing Site 1 prefixes received from the Site 2 CE.
OSPF Down bit with MPLS L3VPN dual PE routers
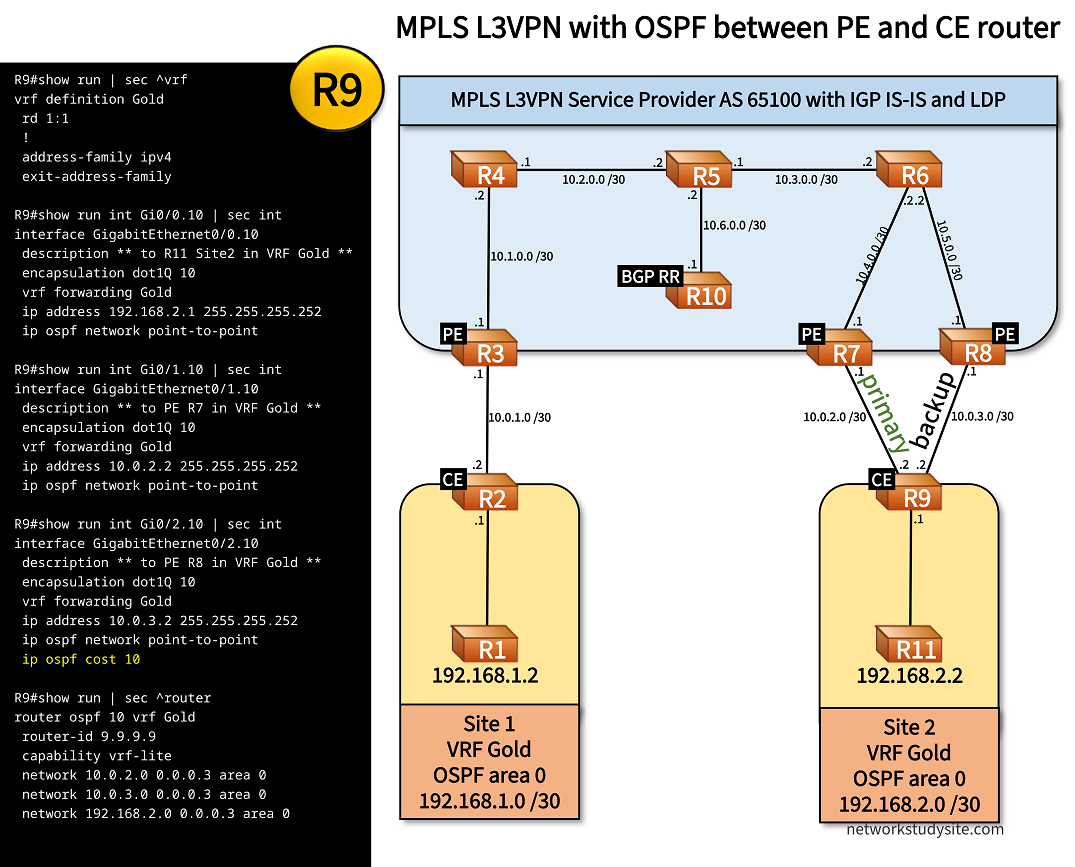
In the following example topology an MPLS L3VPN Service Provider connects two sites. The single CE router R9 on Site 2 is connected to dual PE routers R7 and R8. The PE - CE routing protocol is OSPF. As a result, CE R9 receives two LSAs with the Site 1 prefix (192.168.1.0/30).
When a PE router advertises an OSPF LSA to the CE, it sets the Downward bit to ensure that another PE does not accept the route. Currently, PE R7 sets the Down bit for the Site 1 prefix when advertised to CE R9. As a result, when PE R8 receives the Site 1 prefix back from CE R9 it drops the LSA because of the Downward bit set. This also happens vice versa, and PE R7 does not accept the OSPF LSA advertised by PE R8.
Configuration:
R2 (CE)
R2#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R1 Site1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to R1 Site1 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 192.168.1.1 255.255.255.252
 ip ospf network point-to-point

R2#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R3 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R3 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.2 255.255.255.252
 ip ospf network point-to-point

R2#show run | sec ^router
router ospf 10 vrf Gold
 router-id 2.2.2.2
 capability vrf-lite
 network 10.0.1.0 0.0.0.3 area 0
 network 192.168.1.0 0.0.0.3 area 0
R9 (CE)
R9#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R9#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R11 Site2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R9#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to R11 Site2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 192.168.2.1 255.255.255.252
 ip ospf network point-to-point

R9#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R7 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R9#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R7 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.2 255.255.255.252
 ip ospf network point-to-point

R9#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to PE R8 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R9#show run int Gi0/2.10 | sec int
interface GigabitEthernet0/2.10
 description ** to PE R8 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.3.2 255.255.255.252
 ip ospf network point-to-point
 ip ospf cost 10

R9#show run | sec ^router
router ospf 10 vrf Gold
 router-id 9.9.9.9
 capability vrf-lite
 network 10.0.2.0 0.0.0.3 area 0
 network 10.0.3.0 0.0.0.3 area 0
 network 192.168.2.0 0.0.0.3 area 0
R3 (PE)
R3#show run all | sec ^mpls ip__
mpls ip

R3#show run | sec ^mpls
mpls label range 300 399
mpls ldp router-id Loopback10 force

R3#show run | sec ^vrf
vrf definition Gold
 rd 65100:1
 !
 address-family ipv4
  route-target export 65100:1
  route-target import 65100:2
  route-target import 65100:3
 exit-address-family

R3#show run int Lo10 | sec int
interface Loopback10
 ip address 3.3.3.3 255.255.255.255

R3#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R3#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.1 255.255.255.252
 ip ospf network point-to-point

R3#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R4 **
 ip address 10.1.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R3#show run | sec ^router
router ospf 10 vrf Gold
 router-id 3.3.3.3
 redistribute bgp 65100 subnets
 network 10.0.1.0 0.0.0.3 area 0
router isis
 net 49.0010.0000.0000.0003.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 3.3.3.3
 bgp log-neighbor-changes
 neighbor 10.10.10.10 remote-as 65100
 neighbor 10.10.10.10 update-source Loopback10
 !
 address-family vpnv4
  neighbor 10.10.10.10 activate
  neighbor 10.10.10.10 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  redistribute ospf 10
 exit-address-family
R7 (PE)
R7#show run all | sec ^mpls ip__
mpls ip

R7#show run | sec ^mpls
mpls label range 700 799
mpls ldp router-id Loopback10 force

R7#show run | sec ^vrf
vrf definition Gold
 rd 65100:2
 !
 address-family ipv4
  route-target export 65100:2
  route-target import 65100:1
  route-target import 65100:3
 exit-address-family

R7#show run int Lo10 | sec int
interface Loopback10
 ip address 7.7.7.7 255.255.255.255

R7#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R9 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R7#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R9 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.1 255.255.255.252
 ip ospf network point-to-point

R7#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R6 **
 ip address 10.4.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R7#show run | sec ^router
router ospf 10 vrf Gold
 router-id 7.7.7.7
 redistribute bgp 65100 subnets
 network 10.0.2.0 0.0.0.3 area 0
router isis
 net 49.0010.0000.0000.0007.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 7.7.7.7
 bgp log-neighbor-changes
 neighbor 10.10.10.10 remote-as 65100
 neighbor 10.10.10.10 update-source Loopback10
 !
 address-family vpnv4
  neighbor 10.10.10.10 activate
  neighbor 10.10.10.10 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  redistribute ospf 10
 exit-address-family
R8 (PE)
R8#show run all | sec ^mpls ip__
mpls ip

R8#show run | sec ^mpls
mpls label range 800 899
mpls ldp router-id Loopback10 force

R8#show run | sec ^vrf
vrf definition Gold
 rd 65100:3
 !
 address-family ipv4
  route-target export 65100:3
  route-target import 65100:1
  route-target import 65100:2
 exit-address-family

R8#show run int Lo10 | sec int
interface Loopback10
 ip address 8.8.8.8 255.255.255.255

R8#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R9 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R8#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R9 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.3.1 255.255.255.252
 ip ospf network point-to-point
 ip ospf cost 10

R8#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R6 **
 ip address 10.5.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R8#show run | sec ^router
router ospf 10 vrf Gold
 router-id 8.8.8.8
 redistribute bgp 65100 subnets
 network 10.0.3.0 0.0.0.3 area 0
router isis
 net 49.0010.0000.0000.0008.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 8.8.8.8
 bgp log-neighbor-changes
 neighbor 10.10.10.10 remote-as 65100
 neighbor 10.10.10.10 update-source Loopback10
 !
 address-family vpnv4
  neighbor 10.10.10.10 activate
  neighbor 10.10.10.10 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  redistribute ospf 10
 exit-address-family
R10 (BGP RR)
R10#show run int Lo10 | sec int
interface Loopback10
 ip address 10.10.10.10 255.255.255.255

R10#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R5 **
 ip address 10.6.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R10#show run | sec ^router
router isis
 net 49.0010.0000.0000.0010.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 10.10.10.10
 bgp log-neighbor-changes
 neighbor 3.3.3.3 remote-as 65100
 neighbor 3.3.3.3 update-source Loopback10
 neighbor 7.7.7.7 remote-as 65100
 neighbor 7.7.7.7 update-source Loopback10
 neighbor 8.8.8.8 remote-as 65100
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 3.3.3.3 activate
  neighbor 3.3.3.3 send-community extended
  neighbor 3.3.3.3 route-reflector-client
  neighbor 7.7.7.7 activate
  neighbor 7.7.7.7 send-community extended
  neighbor 7.7.7.7 route-reflector-client
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
  neighbor 8.8.8.8 route-reflector-client
 exit-address-family
R5
R5#show run all | sec ^mpls ip__
mpls ip

R5#show run | sec ^mpls
mpls label range 500 599
mpls ldp router-id Loopback10 force

R5#show run int Lo10 | sec int
interface Loopback10
 ip address 5.5.5.5 255.255.255.255

R5#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R4 **
 ip address 10.2.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R6 **
 ip address 10.3.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to BGP RR R10 **
 ip address 10.6.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run | sec ^router
router isis
 net 49.0010.0000.0000.0005.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R1
R1#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R1#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 192.168.1.2 255.255.255.252
 ip ospf network point-to-point

R1#show run | sec ^router
router ospf 10 vrf Gold
 router-id 1.1.1.1
 capability vrf-lite
 network 192.168.1.0 0.0.0.3 area 0
R11
R11#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R11#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R9 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R11#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R9 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 192.168.2.2 255.255.255.252
 ip ospf network point-to-point

R11#show run | sec ^router
router ospf 10 vrf Gold
 router-id 11.11.11.11
 capability vrf-lite
 network 192.168.2.0 0.0.0.3 area 0
R9#show ip ospf database summary 192.168.1.0

            OSPF Router with ID (9.9.9.9) (Process ID 10)

                Summary Net Link States (Area 0)

  LS age: 271
  Options: (No TOS-capability, DC, Downward)                 « OSPF DN bit is set
  LS Type: Summary Links(Network)
  Link State ID: 192.168.1.0 (summary Network Number)
  Advertising Router: 7.7.7.7                                « PE R7 advertises this LSA
  LS Seq Number: 80000003
  Checksum: 0x70C4
  Length: 28
  Network Mask: /30
        MTID: 0         Metric: 2

  LS age: 271
  Options: (No TOS-capability, DC, Downward)
  LS Type: Summary Links(Network)
  Link State ID: 192.168.1.0 (summary Network Number)
  Advertising Router: 8.8.8.8
  LS Seq Number: 80000003
  Checksum: 0x52DE
  Length: 28
  Network Mask: /30
        MTID: 0         Metric: 2


R9#show ip ospf rib 192.168.1.0

            OSPF Router with ID (9.9.9.9) (Process ID 10)


                Base Topology (MTID 0)

OSPF local RIB
Codes: * - Best, > - Installed in global RIB
LSA: type/LSID/originator

*>  192.168.1.0/30, Inter, cost 3, area 0
     SPF Instance 5, age 01:12:07
      contributing LSA: 3/192.168.1.0/7.7.7.7 (area 0)       « LSA advertised by PE R7
      contributing LSA: 3/192.168.1.0/8.8.8.8 (area 0)       « LSA advertised by PE R8
     Flags: RIB, PartialSPF
      via 10.0.2.1, GigabitEthernet0/1.10 label 1048578
       Flags: RIB
       LSA: 3/192.168.1.0/7.7.7.7
When a CE router receives an OSPF LSA with the DN bit set, it propagates the LSA unchanged. Thus, OSPF neighbors of CE R9 receive the LSA with the DN bit set. The following output is taken from R11.
R11#show ip ospf database summary 192.168.1.0

            OSPF Router with ID (11.11.11.11) (Process ID 10)

                Summary Net Link States (Area 0)

  LS age: 497
  Options: (No TOS-capability, DC, Downward)
  LS Type: Summary Links(Network)
  Link State ID: 192.168.1.0 (summary Network Number)
  Advertising Router: 7.7.7.7
  LS Seq Number: 80000003
  Checksum: 0x70C4
  Length: 28
  Network Mask: /30
        MTID: 0         Metric: 2

  LS age: 496
  Options: (No TOS-capability, DC, Downward)
  LS Type: Summary Links(Network)
  Link State ID: 192.168.1.0 (summary Network Number)
  Advertising Router: 8.8.8.8
  LS Seq Number: 80000003
  Checksum: 0x52DE
  Length: 28
  Network Mask: /30
        MTID: 0         Metric: 2
When a PE router receives an LSA with the DN bit set, it ignores the LSA and does not install it into the OSPF RIB. The following is a debug output taken from PE R8 when it receives an OSPF LSA originated by PE R7 and with the DN bit set.
R8#show log | beg Log Buffer
Log Buffer (8192 bytes):

[...]

OSPF-10 INTER: Check and generate summary LSA into all areas
OSPF-10 INTER: Running spf for summaries area 0
OSPF-10 INTER: Start processing: type 3, LSID 10.0.1.0, mask 255.255.255.252,
OSPF-10 INTER:   adv_rtr 7.7.7.7, age 1313, seq 0x80000003, area 0
OSPF-10 INTER: Downward bit set/Non-backbone LSA               « PE R8 receives LSA with DN bit
OSPF-10 INTER: Start processing: type 3, LSID 192.168.1.0, mask 255.255.255.252,
OSPF-10 INTER:   adv_rtr 7.7.7.7, age 1313, seq 0x80000003, area 0
OSPF-10 INTER: Downward bit set/Non-backbone LSA


R8#show ip ospf database summary 192.168.1.0

            OSPF Router with ID (8.8.8.8) (Process ID 10)

                Summary Net Link States (Area 0)

  LS age: 1574
  Options: (No TOS-capability, DC, Downward)                   « PE R8 receives LSA with DN bit
  LS Type: Summary Links(Network)
  Link State ID: 192.168.1.0 (summary Network Number)
  Advertising Router: 7.7.7.7
  LS Seq Number: 80000003
  Checksum: 0x70C4
  Length: 28
  Network Mask: /30
        MTID: 0         Metric: 2

  LS age: 1572
  Options: (No TOS-capability, DC, Downward)
  LS Type: Summary Links(Network)
  Link State ID: 192.168.1.0 (summary Network Number)
  Advertising Router: 8.8.8.8
  LS Seq Number: 80000003
  Checksum: 0x52DE
  Length: 28
  Network Mask: /30
        MTID: 0         Metric: 2


R8#show ip ospf rib                           « PE R8 does not install LSA with DN bit set

            OSPF Router with ID (8.8.8.8) (Process ID 10)


                Base Topology (MTID 0)

OSPF local RIB
Codes: * - Best, > - Installed in global RIB

*>  10.0.2.0/30, Intra, cost 11, area 0
      via 10.0.3.2, GigabitEthernet0/0.10
*   10.0.3.0/30, Intra, cost 10, area 0, Connected
      via 10.0.3.1, GigabitEthernet0/0.10
*>  192.168.2.0/30, Intra, cost 11, area 0
      via 10.0.3.2, GigabitEthernet0/0.10


R8#show ip route vrf Gold ospf | beg Ga       « PE R8 does not install LSA with DN bit set
Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 4 subnets, 2 masks
O        10.0.2.0/30 [110/11] via 10.0.3.2, 00:05:56, GigabitEthernet0/0.10
      192.168.2.0/30 is subnetted, 1 subnets
O        192.168.2.0 [110/11] via 10.0.3.2, 00:05:56, GigabitEthernet0/0.10
Packet capture OSPF Down bit
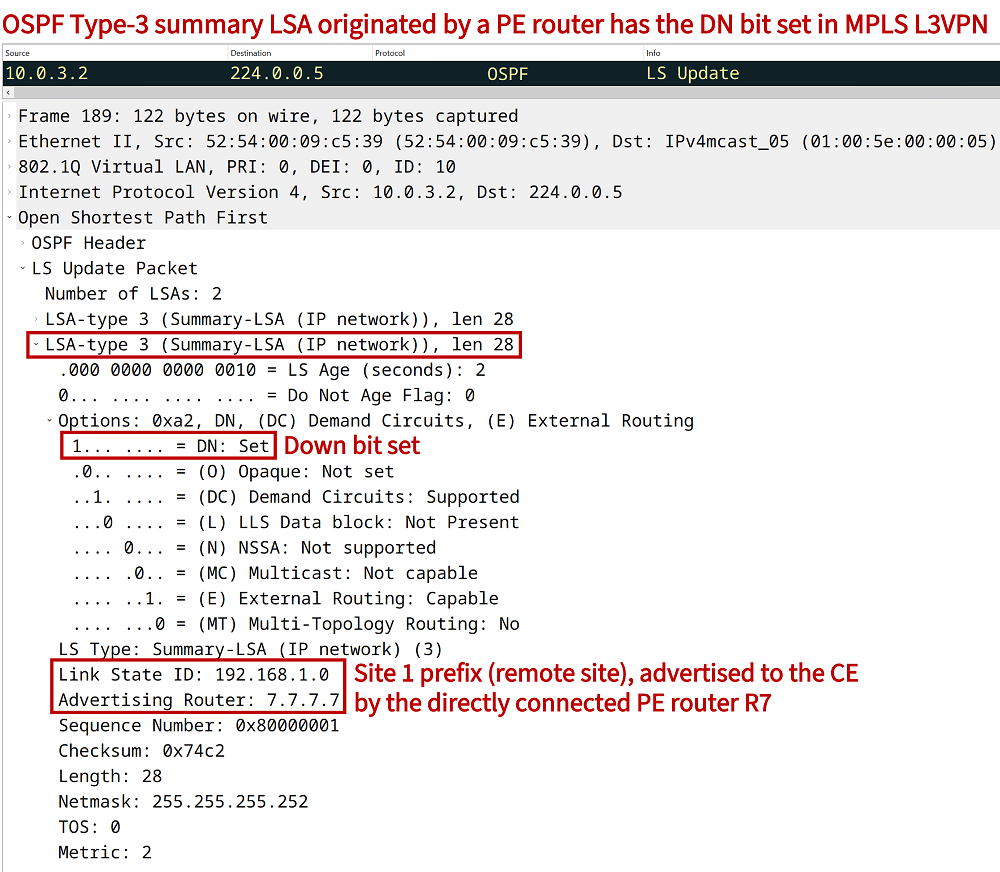
In the OSPF LSA options field the single DN bit is either turned to 1 (Down bit set) or is turned to 0 (Upward bit set). The following packet capture shows an LSA originated by PE R7, and forwarded by CE R9 to the backup PE R8. Upon receiving this LSA the PE R8 ignores the prefix because the DN bit is set. Thus, the Site 1 prefix is not redistributed twice into the MPLS VPN backbone network, and a loop is avoided.