LDP over MPLS Traffic Engineering (TE) Tunnel Configuration
Table of Contents
Jump to section:
What is LDP over MPLS TE?
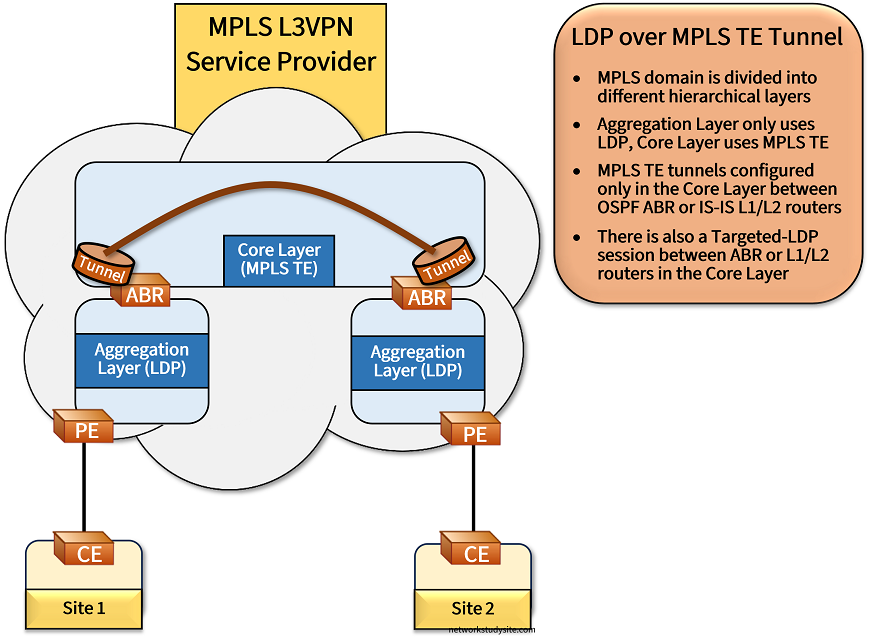
An LDP over MPLS TE solution reduces the number of MPLS Traffic Engineering tunnels in a service provider network. Importantly, MPLS TE tunnels are not configured on the PE routers. Instead, the MPLS backbone network is divided into two functional areas, a Core Layer using MPLS TE and an Aggregation Layer using LDP only.
MPLS TE tunnels are configured only in the Core Layer, on Area Border Routers (ABR). In other words, MPLS TE tunnels are now configured between P (Provider) routers only, and not between PE routers. This solution still allows for MPLS Traffic Engineering and Fast Reroute (FRR) in the Core Layer.
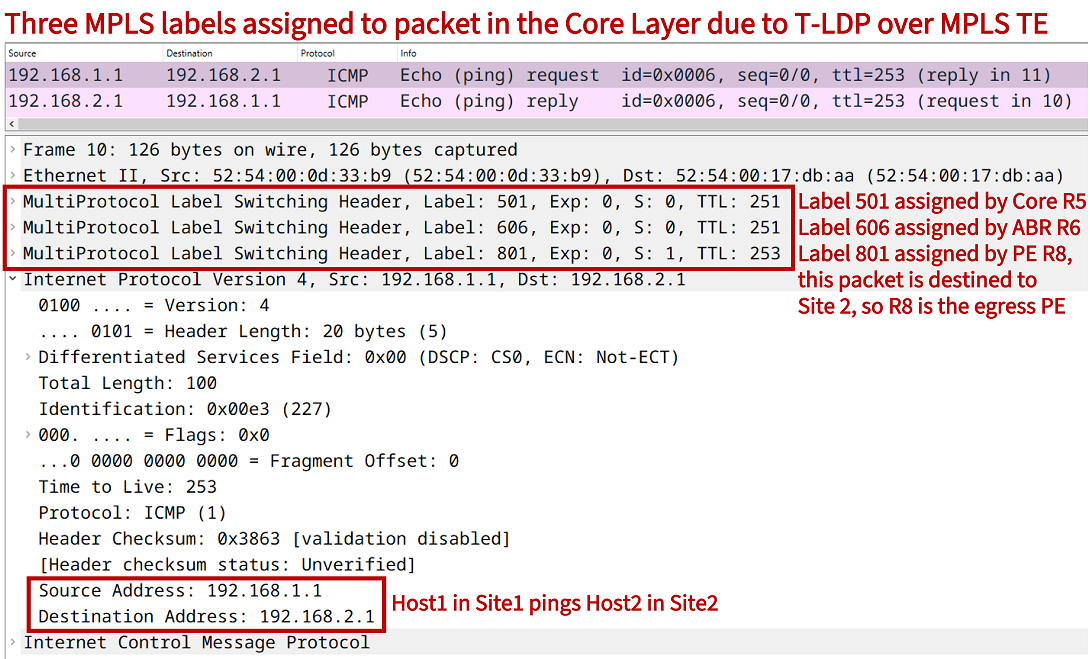
A control plane hierarchy is created in the Core Layer by using a Targeted-LDP session over an MPLS TE tunnel, as a result the label stack includes three MPLS labels. This is shown in the following packet capture. The packet is assigned an IGP next-hop label by a directly connected core device, an MPLS TE tunnel label is assigned by the ABR device, and the egress PE router assigns the VPN service label.
How to configure LDP over MPLS TE?
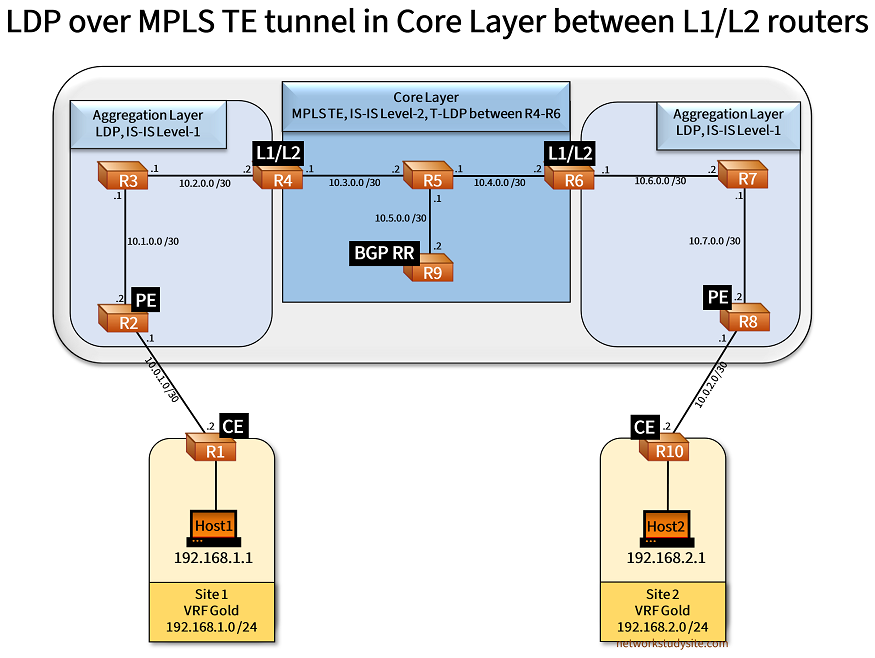
The following example topology connects two sites through an MPLS L3VPN service provider network. The MPLS L3VPN backbone is configured with IS-IS and is divided into the functional areas of a Core and an Aggregation Layer. The IS-IS Level-1/Level-2 routers separate the two areas which use different methods for LSP signaling.
Namely, the Aggregation Layer (where the PE routers are located) only uses Label Distribution Protocol (LDP). Meanwhile, the Core Layer uses MPLS Traffic Engineering (TE) tunnels. In order to create an end-to-end LSP between the two PE routers the following is configured.
- The L1/L2 routers R4 and R6 are connected with an MPLS TE tunnel. However, the MPLS TE tunnel interfaces also have LDP enabled with the mpls ip command. Specifically, a targeted LDP session is configured between R4 and R6 with the example global configuration command mpls ldp neighbor 6.6.6.6 targeted ldp (on R4). The T-LDP session is transported through the MPLS TE tunnel.
- IS-IS route leaking is configured on the L1/L2 routers from Level-2 into Level-1. The PE router /32 loopback prefixes are leaked into each IS-IS Level-1 area, because otherwise the L1/L2 routers only advertise a default route which cannot be used to create an LSP.
Configuration:
R2 (PE)
R2#show run all | sec ^mpls ip$
mpls ip

R2#show run | sec ^mpls
mpls label range 200 299
mpls ldp router-id Loopback10 force

R2#show run int Lo10 | sec int
interface Loopback10
 ip address 2.2.2.2 255.255.255.255

R2#show run | sec ^vrf
vrf definition Gold
 rd 65100:1
 !
 address-family ipv4
  route-target export 65100:1
  route-target import 65100:2
 exit-address-family

R2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R1 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.1 255.255.255.252

R2#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R3 **
 ip address 10.1.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-1
 isis network point-to-point

R2#show run | sec ^router
router isis
 net 49.0010.0000.0000.0002.00
 is-type level-1
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 2.2.2.2
 bgp log-neighbor-changes
 neighbor 9.9.9.9 remote-as 65100
 neighbor 9.9.9.9 update-source Loopback10
 !
 address-family vpnv4
  neighbor 9.9.9.9 activate
  neighbor 9.9.9.9 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.1.0 mask 255.255.255.252
  neighbor 10.0.1.2 remote-as 65001
  neighbor 10.0.1.2 activate
 exit-address-family
R8 (PE)
R8#show run all | sec ^mpls ip$
mpls ip

R8#show run | sec ^mpls
mpls label range 800 899
mpls ldp router-id Loopback10 force

R8#show run int Lo10 | sec int
interface Loopback10
 ip address 8.8.8.8 255.255.255.255

R8#show run | sec ^vrf
vrf definition Gold
 rd 65100:2
 !
 address-family ipv4
  route-target export 65100:2
  route-target import 65100:1
 exit-address-family

R8#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R10 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R8#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R10 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.1 255.255.255.252

R8#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R7 **
 ip address 10.7.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-1
 isis network point-to-point

R8#show run | sec ^router
router isis
 net 49.0020.0000.0000.0008.00
 is-type level-1
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 8.8.8.8
 bgp log-neighbor-changes
 neighbor 9.9.9.9 remote-as 65100
 neighbor 9.9.9.9 update-source Loopback10
 !
 address-family vpnv4
  neighbor 9.9.9.9 activate
  neighbor 9.9.9.9 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.2.0 mask 255.255.255.252
  neighbor 10.0.2.2 remote-as 65002
  neighbor 10.0.2.2 activate
 exit-address-family
R4 (IS-IS L1/L2, ABR)
R4#show run all | sec ^mpls ip__
mpls ip

R4#show run | sec ^mpls
mpls label range 400 499
mpls ldp neighbor 6.6.6.6 targeted ldp
mpls traffic-eng tunnels
mpls ldp router-id Loopback10 force

R4#show run int Lo10 | sec int
interface Loopback10
 ip address 4.4.4.4 255.255.255.255

R4#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R3 **
 ip address 10.2.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-1
 isis network point-to-point

R4#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.3.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R4#show run int Tu10 | sec int
interface Tunnel10
 description ** MPLS TE tunnel to ABR R6 **
 ip unnumbered Loopback10
 mpls ip
 tunnel mode mpls traffic-eng
 tunnel destination 6.6.6.6
 tunnel mpls traffic-eng autoroute announce
 tunnel mpls traffic-eng priority 1 1
 tunnel mpls traffic-eng bandwidth 50
 tunnel mpls traffic-eng path-option 10 dynamic
 no routing dynamic

R4#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0004.00
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 redistribute isis ip level-2 into level-1 route-map RM-REDIST-PE-R8
 passive-interface Loopback10

R4#show run | sec ^route-map
route-map RM-REDIST-PE-R8 permit 10
 match ip address prefix-list PL-REDIST-PE-R8

R4#show run | sec ^ip prefix
ip prefix-list PL-REDIST-PE-R8 seq 5 permit 8.8.8.8/32
R6 (IS-IS L1/L2, ABR)
R6#show run all | sec ^mpls ip__
mpls ip

R6#show run | sec ^mpls
mpls label range 600 699
mpls ldp neighbor 4.4.4.4 targeted ldp
mpls traffic-eng tunnels
mpls ldp router-id Loopback10 force

R6#show run int Lo10 | sec int
interface Loopback10
 ip address 6.6.6.6 255.255.255.255

R6#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R7 **
 ip address 10.6.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-1
 isis network point-to-point

R6#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.4.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R6#show run int Tu10 | sec int
interface Tunnel10
 description ** MPLS TE tunnel to ABR R4 **
 ip unnumbered Loopback10
 mpls ip
 tunnel mode mpls traffic-eng
 tunnel destination 4.4.4.4
 tunnel mpls traffic-eng autoroute announce
 tunnel mpls traffic-eng priority 1 1
 tunnel mpls traffic-eng bandwidth 50
 tunnel mpls traffic-eng path-option 10 dynamic
 no routing dynamic

R6#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0020.0000.0000.0006.00
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 redistribute isis ip level-2 into level-1 route-map RM-REDIST-PE-R2
 passive-interface Loopback10

R6#show run | sec ^route-map
route-map RM-REDIST-PE-R2 permit 10
 match ip address prefix-list PL-REDIST-PE-R2

R6#show run | sec ^ip prefix
ip prefix-list PL-REDIST-PE-R2 seq 5 permit 2.2.2.2/32
R9 (BGP RR)
R9#show run int Lo10 | sec int
interface Loopback10
 ip address 9.9.9.9 255.255.255.255

R9#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R5 **
 ip address 10.5.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R9#show run | sec ^router
router isis
 net 49.0005.0000.0000.0009.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 9.9.9.9
 bgp log-neighbor-changes
 neighbor 2.2.2.2 remote-as 65100
 neighbor 2.2.2.2 update-source Loopback10
 neighbor 8.8.8.8 remote-as 65100
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 2.2.2.2 activate
  neighbor 2.2.2.2 send-community extended
  neighbor 2.2.2.2 route-reflector-client
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
  neighbor 8.8.8.8 route-reflector-client
 exit-address-family
R3
R3#show run all | sec ^mpls ip__
mpls ip

R3#show run | sec ^mpls
mpls label range 300 399
mpls ldp router-id Loopback10 force

R3#show run int Lo10 | sec int
interface Loopback10
 ip address 3.3.3.3 255.255.255.255

R3#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R2 **
 ip address 10.1.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-1
 isis network point-to-point

R3#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ABR R4 **
 ip address 10.2.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-1
 isis network point-to-point

R3#show run | sec ^router
router isis
 net 49.0010.0000.0000.0003.00
 is-type level-1
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R5
R5#show run | sec ^mpls
mpls label range 500 599
mpls traffic-eng tunnels

R5#show run int Lo10 | sec int
interface Loopback10
 ip address 5.5.5.5 255.255.255.255

R5#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to ABR R4 **
 ip address 10.3.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R5#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ABR R6 **
 ip address 10.4.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R5#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to BGP RR R9 **
 ip address 10.5.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0005.0000.0000.0005.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R1 (CE)
R1#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Host1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R1#show run int Gi0/0.1 | sec int
interface GigabitEthernet0/0.1
 description ** to Host1 in VRF Gold (VLAN 1) **
 encapsulation dot1Q 1 native
 vrf forwarding Gold
 ip address 192.168.1.2 255.255.255.0

R1#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R1#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.2 255.255.255.252

R1#show run | sec ^router
router bgp 65001
 bgp router-id 1.1.1.1
 bgp log-neighbor-changes
 !
 address-family ipv4 vrf Gold
  network 192.168.1.0
  neighbor 10.0.1.1 remote-as 65100
  neighbor 10.0.1.1 activate
 exit-address-family
R10 (CE)
R10#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R10#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Host2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R10#show run int Gi0/0.1 | sec int
interface GigabitEthernet0/0.1
 description ** to Host2 in VRF Gold (VLAN 1) **
 encapsulation dot1Q 1 native
 vrf forwarding Gold
 ip address 192.168.2.2 255.255.255.0

R10#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R8 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R10#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R8 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.2 255.255.255.252

R10#show run | sec ^router
router bgp 65002
 bgp router-id 10.10.10.10
 bgp log-neighbor-changes
 !
 address-family ipv4 vrf Gold
  network 192.168.2.0
  neighbor 10.0.2.1 remote-as 65100
  neighbor 10.0.2.1 activate
 exit-address-family
Host1
Host1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R1 **
 ip address 192.168.1.1 255.255.255.0
 duplex auto
 speed auto
 media-type rj45

Host1#show run | sec ^ip route
ip route 0.0.0.0 0.0.0.0 192.168.1.2
Host1#ping 192.168.2.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 192.168.2.1, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 49/50/53 ms          « There is connectivity between the Site 1 and Site 2


Host1#trace 192.168.2.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.2.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.2 2 msec
  2 10.0.1.1 29 msec
  3 10.1.0.1 [MPLS: Labels 304/804 Exp 0] 51 msec
  4 10.2.0.2 [MPLS: Labels 408/804 Exp 0] 51 msec
  5 10.3.0.2 [MPLS: Labels 501/608/804 Exp 0] 51 msec              « Three MPLS labels assigned in Core Layer
  6 10.4.0.2 [MPLS: Labels 608/804 Exp 0] 49 msec
  7 10.6.0.2 [MPLS: Labels 703/804 Exp 0] 50 msec
  8 10.0.2.1 [MPLS: Label 804 Exp 0] 28 msec                       « VPN Service Label assigned by PE R8
  9 10.0.2.2 50 msec
 10 192.168.2.1 51 msec


R2#show ip bgp vpnv4 rd 65100:2 192.168.2.0
BGP routing table entry for 65100:2:192.168.2.0/24, version 5      « Site 2 VPNv4 prefix received on PE R2
Paths: (1 available, best #1, no table)
  Flag: 0x100
  Not advertised to any peer
  Refresh Epoch 1
  65002
    8.8.8.8 (metric 60) (via default) from 9.9.9.9 (9.9.9.9)       « MP-BGP route originated by PE R8
      Origin IGP, metric 0, localpref 100, valid, internal, best
      Extended Community: RT:65100:2
      Originator: 8.8.8.8, Cluster list: 9.9.9.9
      mpls labels in/out nolabel/804                               « PE R8 assigns VPN Service Label 804
      rx pathid: 0, tx pathid: 0x0
      Updated on Apr 26 2024 17:38:20 UTC
Notice in the above outputs that Site 1 can communicate with Site 2 through the MPLS L3VPN network, however there are three MPLS labels assigned in the Core Layer. The label ranges are configured so that the assigning routers can be identified, for example R5 uses the range 500 - 599, R6 uses 600 - 699 and so on.
Consequently, it is visible that between the L1/L2 routers a T-LDP session is encapsulated in an MPLS TE tunnel creating two additional labels next to the VPN Service Label 804. Also, notice in the following outputs that the PE routers receive the inter-area IS-IS prefix of each other's loopback IP address. The prefixes are leaked on the L1/L2 routers into the Level-1 areas.
R2#show ip route isis |  beg Ga
Gateway of last resort is 10.1.0.1 to network 0.0.0.0

i*L1  0.0.0.0/0 [115/20] via 10.1.0.1, 00:10:30, GigabitEthernet2
      3.0.0.0/32 is subnetted, 1 subnets
i L1     3.3.3.3 [115/10] via 10.1.0.1, 00:10:30, GigabitEthernet2
      4.0.0.0/32 is subnetted, 1 subnets
i L1     4.4.4.4 [115/20] via 10.1.0.1, 00:10:30, GigabitEthernet2
      8.0.0.0/32 is subnetted, 1 subnets
i ia     8.8.8.8 [115/60] via 10.1.0.1, 00:10:17, GigabitEthernet2      « PE R8 IP received on PE R2


R2#show ip route 8.8.8.8
Routing entry for 8.8.8.8/32
  Known via "isis", distance 115, metric 60, type inter area            « This an inter area leaked prefix
  Redistributing via isis
  Last update from 10.1.0.1 on GigabitEthernet2, 00:10:26 ago
  Routing Descriptor Blocks:
  * 10.1.0.1, from 4.4.4.4, 00:10:26 ago, via GigabitEthernet2          « PE R8 IP originated by L1/L2 router R4
      Route metric is 60, traffic share count is 1


R2#trace 8.8.8.8 source 2.2.2.2 probe 1
Type escape sequence to abort.
Tracing the route to 8.8.8.8
VRF info: (vrf in name/id, vrf out name/id)
  1 10.1.0.1 [MPLS: Label 304 Exp 0] 10 msec
  2 10.2.0.2 [MPLS: Label 408 Exp 0] 6 msec
  3 10.3.0.2 [MPLS: Labels 501/608 Exp 0] 7 msec                        « MPLS transport labels (not VPN label) assigned in Core
  4 10.4.0.2 [MPLS: Label 608 Exp 0] 6 msec
  5 10.6.0.2 [MPLS: Label 703 Exp 0] 4 msec
  6 10.7.0.2 32 msec
The following output highlights the MPLS TE tunnel that is configured in the Core Layer. The advantage of this design is that the MPLS TE tunnels only need to be configured in the Core Layer, reducing the overall number of tunnels to administer between each PE router (in a large backbone network). Furthermore, the following output includes the Targeted-LDP session created between the L1/L2 routers in the Core Layer.
R4#show mpls traffic-eng tunnels brief
Signalling Summary:
    LSP Tunnels Process:            running
    Passive LSP Listener:           running
    RSVP Process:                   running
    Forwarding:                     enabled
    Periodic reoptimization:        every 3600 seconds, next in 2636 seconds
    Periodic FRR Promotion:         Not Running
    Periodic auto-bw collection:    every 300 seconds, next in 236 seconds
TUNNEL NAME                      DESTINATION      UP IF      DOWN IF    STATE/PROT
** MPLS TE tunnel to ABR R6 ...  6.6.6.6          -         Gi0/1     up/up          « MPLS TE tunnel is up
** MPLS TE tunnel to ABR R4 ...  4.4.4.4          Gi0/1      -          up/up
Displayed 1 (of 1) heads, 0 (of 0) midpoints, 1 (of 1) tails


R4#show mpls ldp neighbor
    Peer LDP Ident: 3.3.3.3:0; Local LDP Ident 4.4.4.4:0
        TCP connection: 3.3.3.3.646 - 4.4.4.4.48141
        State: Oper; Msgs sent/rcvd: 33/31; Downstream
        Up time: 00:18:48
        LDP discovery sources:
          GigabitEthernet0/0, Src IP addr: 10.2.0.1
        Addresses bound to peer LDP Ident:
          10.1.0.1        3.3.3.3         10.2.0.1
    Peer LDP Ident: 6.6.6.6:0; Local LDP Ident 4.4.4.4:0
        TCP connection: 6.6.6.6.14598 - 4.4.4.4.646
        State: Oper; Msgs sent/rcvd: 34/34; Downstream
        Up time: 00:18:46
        LDP discovery sources:
          Targeted Hello 4.4.4.4 -> 6.6.6.6, active, passive                  « Target-Hello adjacency is established between R4 - R6
        Addresses bound to peer LDP Ident:
          6.6.6.6         10.6.0.1        10.4.0.2