PE - CE Routing with EIGRP in MPLS Layer-3 VPN Tutorial
Table of Contents
- How to configure EIGRP as the PE-CE routing protocol? ‹
- Packet capture BGP VPNv4 Update with prefix from EIGRP ‹
- Configuring Site of Origin (SoO) extended community ‹
- Download section ‹
How to configure EIGRP as the PE-CE routing protocol?
In the following example scenario, EIGRP is configured as the PE - CE routing protocol in an MPLS Layer-3 VPN. The following are important aspects that make this solution work.
- The same EIGRP autonomous system (AS) number is configured on both sites and between the PE - CE. This is important so that EIGRP prefixes are received as internal routes on the CE devices.
- EIGRP is configured on the PE routers, and two-way route redistribution is configured between EIGRP and BGP on the PEs.
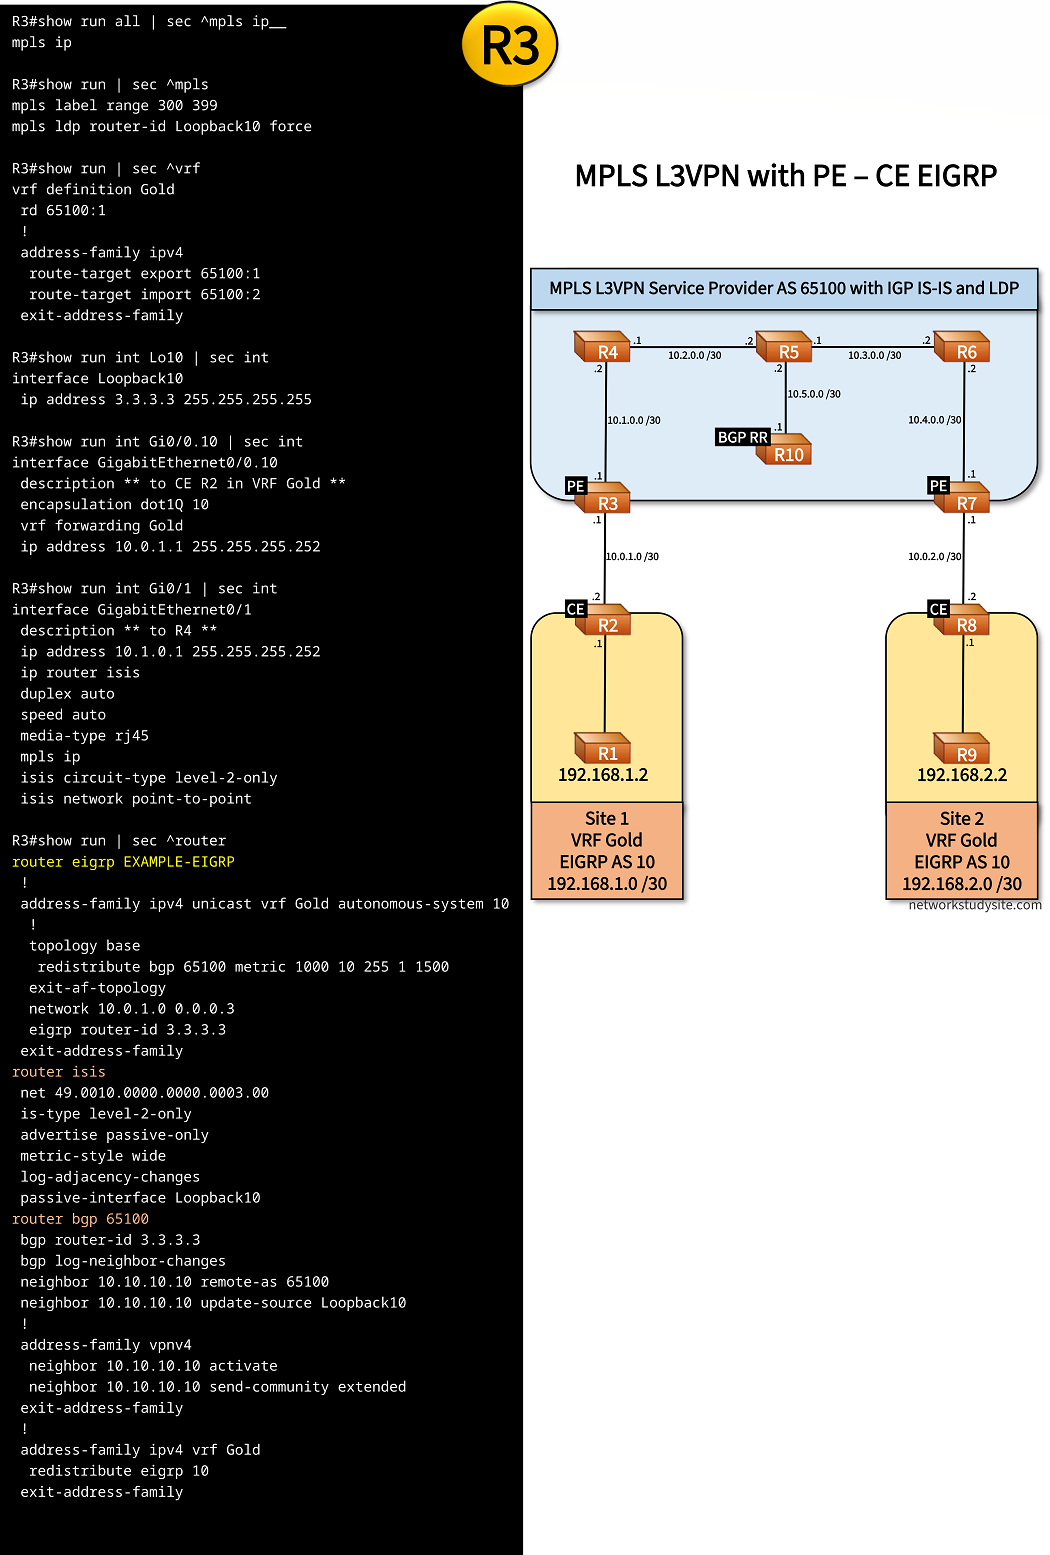
Configuration:
R3 (PE)
R3#show run all | sec ^mpls ip__
mpls ip

R3#show run | sec ^mpls
mpls label range 300 399
mpls ldp router-id Loopback10 force

R3#show run | sec ^vrf
vrf definition Gold
 rd 65100:1
 !
 address-family ipv4
  route-target export 65100:1
  route-target import 65100:2
 exit-address-family

R3#show run int Lo10 | sec int
interface Loopback10
 ip address 3.3.3.3 255.255.255.255

R3#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R3#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.1 255.255.255.252

R3#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R4 **
 ip address 10.1.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R3#show run | sec ^router
router eigrp EXAMPLE-EIGRP
 !
 address-family ipv4 unicast vrf Gold autonomous-system 10
  !
  topology base
   redistribute bgp 65100 metric 1000 10 255 1 1500
  exit-af-topology
  network 10.0.1.0 0.0.0.3
  eigrp router-id 3.3.3.3
 exit-address-family
router isis
 net 49.0010.0000.0000.0003.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 3.3.3.3
 bgp log-neighbor-changes
 neighbor 10.10.10.10 remote-as 65100
 neighbor 10.10.10.10 update-source Loopback10
 !
 address-family vpnv4
  neighbor 10.10.10.10 activate
  neighbor 10.10.10.10 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  redistribute eigrp 10
 exit-address-family
R7 (PE)
R7#show run all | sec ^mpls ip__
mpls ip

R7#show run | sec ^mpls
mpls label range 700 799
mpls ldp router-id Loopback10 force

R7#show run | sec ^vrf
vrf definition Gold
 rd 65100:2
 !
 address-family ipv4
  route-target export 65100:2
  route-target import 65100:1
 exit-address-family

R7#show run int Lo10 | sec int
interface Loopback10
 ip address 7.7.7.7 255.255.255.255

R7#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R8 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R7#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R8 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.1 255.255.255.252

R7#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R6 **
 ip address 10.4.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R7#show run | sec ^router
router eigrp EXAMPLE-EIGRP
 !
 address-family ipv4 unicast vrf Gold autonomous-system 10
  !
  topology base
   redistribute bgp 65100 metric 1000 10 255 1 1500
  exit-af-topology
  network 10.0.2.0 0.0.0.3
  eigrp router-id 7.7.7.7
 exit-address-family
router isis
 net 49.0010.0000.0000.0007.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 7.7.7.7
 bgp log-neighbor-changes
 neighbor 10.10.10.10 remote-as 65100
 neighbor 10.10.10.10 update-source Loopback10
 !
 address-family vpnv4
  neighbor 10.10.10.10 activate
  neighbor 10.10.10.10 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  redistribute eigrp 10
 exit-address-family
R2 (CE)
R2#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R1 Site1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to R1 Site1 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 192.168.1.1 255.255.255.252

R2#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R3 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R3 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.2 255.255.255.252

R2#show run | sec ^router
router eigrp EXAMPLE-EIGRP
 !
 address-family ipv4 unicast vrf Gold autonomous-system 10
  !
  topology base
  exit-af-topology
  network 10.0.1.0 0.0.0.3
  network 192.168.1.0 0.0.0.3
  eigrp router-id 2.2.2.2
 exit-address-family
R8 (CE)
R8#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R8#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R9 Site2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R8#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to R9 Site2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 192.168.2.1 255.255.255.252

R8#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R7 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R8#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R7 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.2 255.255.255.252

R8#show run | sec ^router
router eigrp EXAMPLE-EIGRP
 !
 address-family ipv4 unicast vrf Gold autonomous-system 10
  !
  topology base
  exit-af-topology
  network 10.0.2.0 0.0.0.3
  network 192.168.2.0 0.0.0.3
  eigrp router-id 8.8.8.8
 exit-address-family
R10 (BGP RR)
R10#show run int Lo10 | sec int
interface Loopback10
 ip address 10.10.10.10 255.255.255.255

R10#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R5 **
 ip address 10.5.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R10#show run | sec ^router
router isis
 net 49.0010.0000.0000.0010.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 10.10.10.10
 bgp log-neighbor-changes
 neighbor 3.3.3.3 remote-as 65100
 neighbor 3.3.3.3 update-source Loopback10
 neighbor 7.7.7.7 remote-as 65100
 neighbor 7.7.7.7 update-source Loopback10
 !
 address-family vpnv4
  neighbor 3.3.3.3 activate
  neighbor 3.3.3.3 send-community extended
  neighbor 3.3.3.3 route-reflector-client
  neighbor 7.7.7.7 activate
  neighbor 7.7.7.7 send-community extended
  neighbor 7.7.7.7 route-reflector-client
 exit-address-family
R5
R5#show run all | sec ^mpls ip__
mpls ip

R5#show run | sec ^mpls
mpls label range 500 599
mpls ldp router-id Loopback10 force

R5#show run int Lo10 | sec int
interface Loopback10
 ip address 5.5.5.5 255.255.255.255

R5#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R4 **
 ip address 10.2.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R6 **
 ip address 10.3.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to BGP RR R10 **
 ip address 10.5.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run | sec ^router
router isis
 net 49.0010.0000.0000.0005.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R4
R4#show run all | sec ^mpls ip__
mpls ip

R4#show run | sec ^mpls
mpls label range 400 499
mpls ldp router-id Loopback10 force

R4#show run int Lo10 | sec int
interface Loopback10
 ip address 4.4.4.4 255.255.255.255

R4#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R3 **
 ip address 10.1.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.2.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run | sec ^router
router isis
 net 49.0010.0000.0000.0004.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R1
R1#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R1#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 192.168.1.2 255.255.255.252

R1#show run | sec ^router
router eigrp EXAMPLE-EIGRP
 !
 address-family ipv4 unicast vrf Gold autonomous-system 10
  !
  topology base
  exit-af-topology
  network 192.168.1.0 0.0.0.3
  eigrp router-id 1.1.1.1
 exit-address-family
R1#ping vrf Gold 192.168.2.2
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 192.168.2.2, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 47/48/49 ms           « Site1 can reach Site2 through the MPLS L3VPN


R1#trace vrf Gold 192.168.2.2 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.2.2
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.1 2 msec
  2 10.0.1.1 23 msec
  3 10.1.0.2 [MPLS: Labels 405/712 Exp 0] 47 msec               « MPLS label stack assigned
  4 10.2.0.2 [MPLS: Labels 506/712 Exp 0] 47 msec
  5 10.3.0.2 [MPLS: Labels 602/712 Exp 0] 48 msec
  6 10.0.2.1 [MPLS: Label 712 Exp 0] 26 msec                    « PE router R7 assigns VPN Service Label
  7 10.0.2.2 48 msec
  8 192.168.2.2 48 msec


R9#trace vrf Gold 192.168.1.2 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.1.2
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.2.1 2 msec
  2 10.0.2.1 24 msec
  3 10.4.0.2 [MPLS: Labels 605/310 Exp 0] 49 msec
  4 10.3.0.1 [MPLS: Labels 504/310 Exp 0] 48 msec
  5 10.2.0.1 [MPLS: Labels 402/310 Exp 0] 50 msec
  6 10.0.1.1 [MPLS: Label 310 Exp 0] 27 msec
  7 10.0.1.2 49 msec
  8 192.168.1.2 50 msec


R2#show ip route vrf Gold eigrp | beg Ga
Gateway of last resort is not set

      10.0.0.0/8 is variably subnetted, 3 subnets, 2 masks
D        10.0.2.0/30 [90/15360] via 10.0.1.1, 00:44:40, GigabitEthernet0/1.10         « EIGRP internal routes received on CE
      192.168.2.0/30 is subnetted, 1 subnets
D        192.168.2.0 [90/20480] via 10.0.1.1, 00:44:08, GigabitEthernet0/1.10


R2#show ip route vrf Gold 192.168.2.0 255.255.255.252

Routing Table: Gold
Routing entry for 192.168.2.0/30
  Known via "eigrp 10", distance 90, metric 20480, type internal     « CE R2 receives Site 2 route as internal
  Redistributing via eigrp 10
  Last update from 10.0.1.1 on GigabitEthernet0/1.10, 00:46:10 ago
  Routing Descriptor Blocks:
  * 10.0.1.1, from 10.0.1.1, 00:46:10 ago, via GigabitEthernet0/1.10
      Route metric is 20480, traffic share count is 1
      Total delay is 30 microseconds, minimum bandwidth is 1000000 Kbit
      Reliability 255/255, minimum MTU 1500 bytes
      Loading 1/255, Hops 2


R1#show ip route vrf Gold eigrp | beg Ga
Gateway of last resort is not set

      10.0.0.0/30 is subnetted, 2 subnets
D        10.0.1.0 [90/15360] via 192.168.1.1, 00:41:45, GigabitEthernet0/0.10
D        10.0.2.0 [90/20480] via 192.168.1.1, 00:41:45, GigabitEthernet0/0.10
      192.168.2.0/30 is subnetted, 1 subnets
D        192.168.2.0
           [90/25600] via 192.168.1.1, 00:41:45, GigabitEthernet0/0.10
Packet capture BGP VPNv4 Update with prefix from EIGRP
When EIGRP prefixes are redistributed into the Multiprotocol-BGP VPNv4 address-family, there are several details included in the routing updates. The following output is shown from the PE router R3.
R3#show ip bgp vpnv4 rd 65100:2 192.168.2.0
BGP routing table entry for 65100:2:192.168.2.0/30, version 40               « Site 2 BGP VPNv4 route
Paths: (1 available, best #1, no table)
  Not advertised to any peer
  Refresh Epoch 1
  Local
    7.7.7.7 (metric 40) (via default) from 10.10.10.10 (10.10.10.10)
      Origin incomplete, metric 15360, localpref 100, valid, internal, best
      Extended Community: RT:65100:2 Cost:pre-bestpath:128:15360             « Route Target export value configured on PE R7
        0x8800:32768:0 0x8801:10:512 0x8802:65281:2560 0x8803:65281:1500
        0x8806:0:134744072
      Originator: 7.7.7.7, Cluster list: 10.10.10.10                         « Prefix originated by PE R7
      mpls labels in/out nolabel/712                                         « PE R7 assigns VPN Service Label
      rx pathid: 0, tx pathid: 0x0
As visible there are a variety of BGP Extended Communities assigned in addition to the Route Target export value. These additional extended communities are added on the PE R7, after EIGRP routes are imported into BGP, and advertised as MP-BGP VPNv4 prefixes. For example, the BGP Cost Community appears after the RT, and is a way to influence path selection in MPLS L3VPN networks using EIGRP as the PE - CE protocol. The following packet capture shows further details.
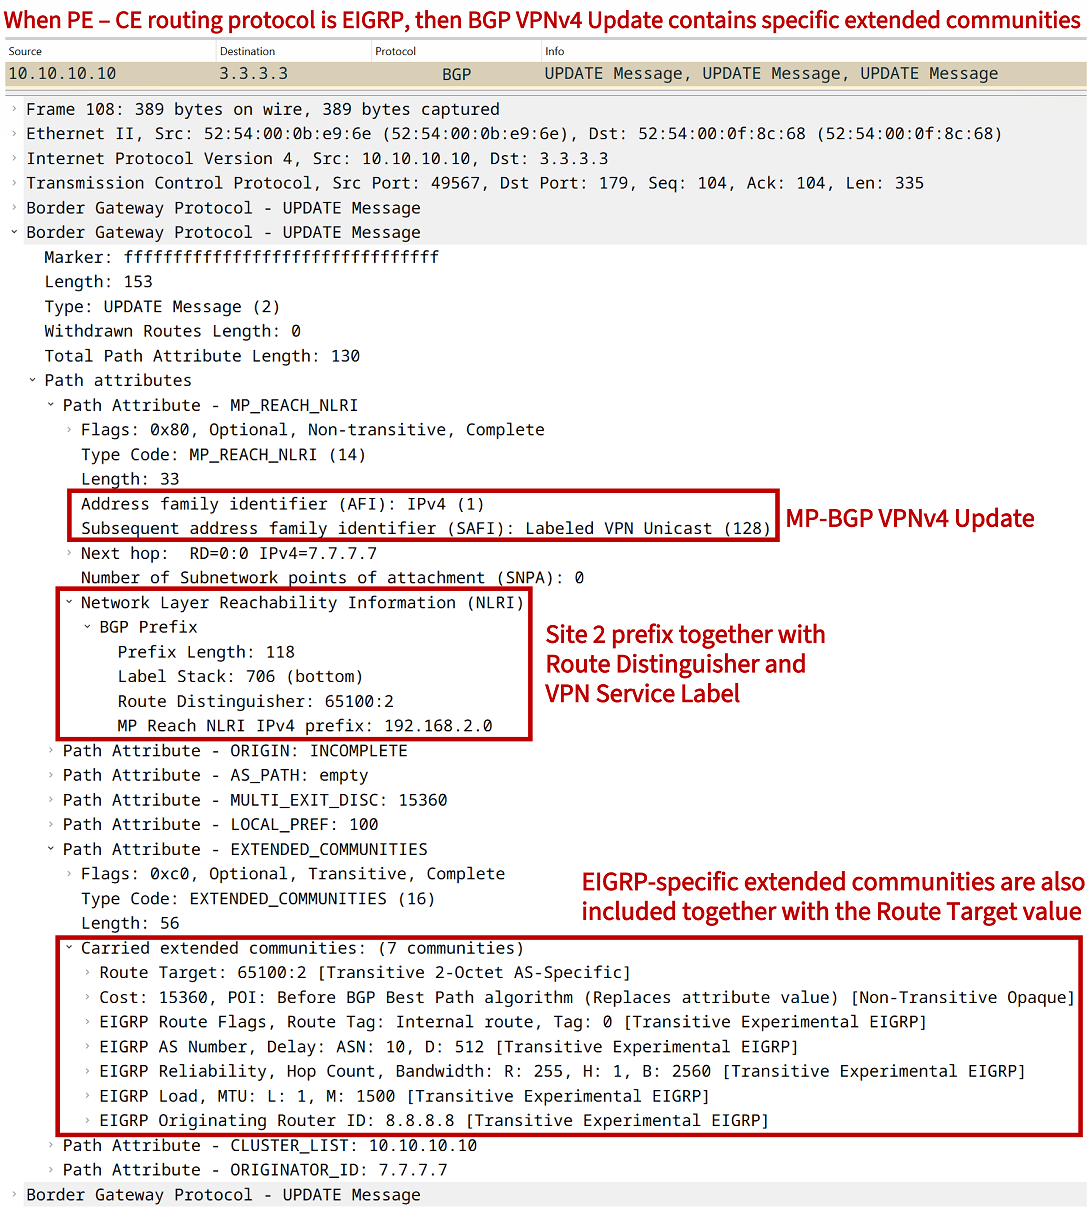
Configuring Site of Origin (SoO) extended community
Site of Origin is a BGP extended community attribute that can be used in an MPLS L3VPN for loop prevention or to avoid having routes redistributed into the same routing protocol twice. SoO can also be used for route filtering as shown in the following example. With EIGRP as the PE - CE routing protocol, Site 2 routes are assigned the SoO value 65100:200 on the PE R7. In turn, the CE R2 blocks any routes that have the SoO value 65100:200 assigned. Thus, Site 1 no longer receives Site 2 routes from CE R2.
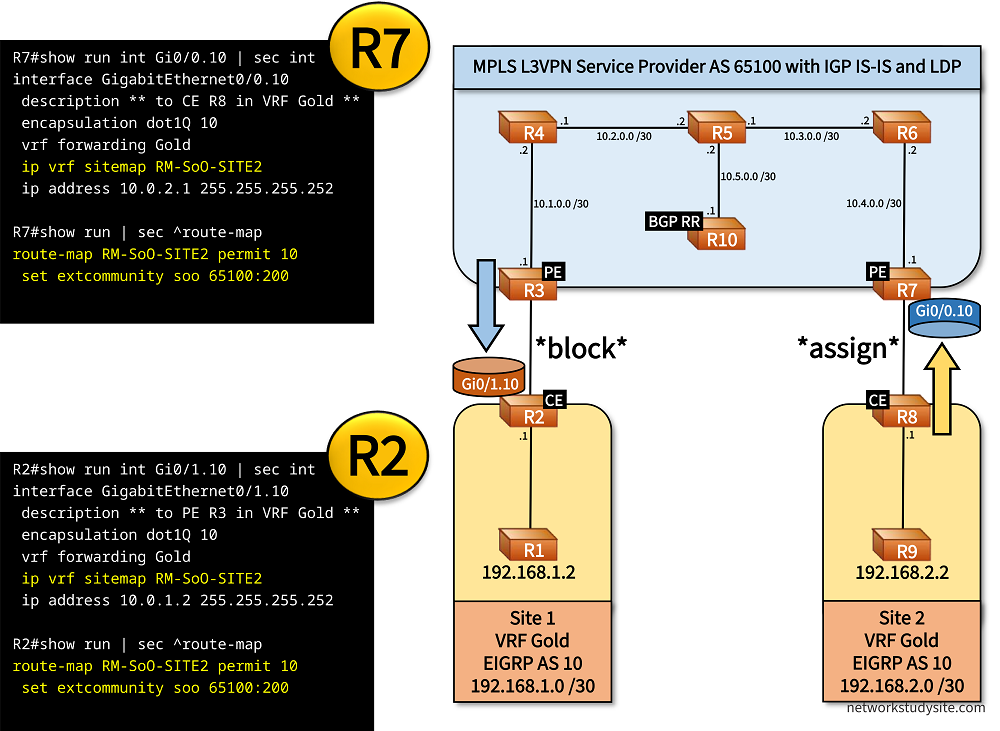
Configuration:
R7 (PE)
R7#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R8 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip vrf sitemap RM-SoO-SITE2
 ip address 10.0.2.1 255.255.255.252

R7#show run | sec ^route-map
route-map RM-SoO-SITE2 permit 10
 set extcommunity soo 65100:200
R2 (CE)
R2#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R3 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip vrf sitemap RM-SoO-SITE2
 ip address 10.0.1.2 255.255.255.252

R2#show run | sec ^route-map
route-map RM-SoO-SITE2 permit 10
 set extcommunity soo 65100:200
R3#show ip bgp vpnv4 rd 65100:2 192.168.2.0
BGP routing table entry for 65100:2:192.168.2.0/30, version 15
Paths: (1 available, best #1, no table)
  Not advertised to any peer
  Refresh Epoch 2
  Local
    7.7.7.7 (metric 40) (via default) from 10.10.10.10 (10.10.10.10)
      Origin incomplete, metric 15360, localpref 100, valid, internal, best
      Extended Community: SoO:65100:200 RT:65100:2                   « SoO value added to BGP VPNv4 route
        Cost:pre-bestpath:128:15360 0x8800:32768:0 0x8801:10:512
        0x8802:65281:2560 0x8803:65281:1500 0x8806:0:134744072
      Originator: 7.7.7.7, Cluster list: 10.10.10.10
      mpls labels in/out nolabel/707
      rx pathid: 0, tx pathid: 0x0


R1#show ip route vrf Gold eigrp | beg Ga                             « Site 1 R1 does not receive Site 2 routes
Gateway of last resort is not set

      10.0.0.0/30 is subnetted, 1 subnets
D        10.0.1.0 [90/15360] via 192.168.1.1, 03:09:50, GigabitEthernet0/0.10
An SoO value can also be filtered on a PE router by creating an extended community-list shown in the following output. Further actions can then be configured under a route-map. Also, routes that match the extended community-list can be viewed.
R3>
R3>enable
R3#configure terminal
Enter configuration commands, one per line.  End with CNTL/Z.
R3(config)#
R3(config)#ip extcommunity-list standard CL-SoO-Site2 permit soo 65100:200
R3(config)#
R3(config)#exit
R3#
R3#show ip bgp vpnv4 rd 65100:2 extcommunity-list CL-SoO-Site2 | begin Network
     Network          Next Hop            Metric LocPrf Weight Path
Route Distinguisher: 65100:2
 *>i  10.0.2.0/30      7.7.7.7                  0    100      0 ?
 *>i  192.168.2.0/30   7.7.7.7              15360    100      0 ?