MPLS TE Autotunnel Primary, Backup and Mesh Group for L3VPN
Table of Contents
- What are the different types of MPLS TE autotunnels? ‹
- Configuring MPLS TE autotunnel primary ‹
- Configuring MPLS TE autotunnel backup ‹
- Configuring MPLS TE autotunnel mesh ‹
- Download section ‹
What are the different types of MPLS TE autotunnels?
The autotunnel feature reduces the administrative tasks related to MPLS Traffic Engineering (TE) tunnel configurations. A variety of MPLS TE tunnels can be dynamically established using autotunnels instead of manually creating each individual tunnel interface. The following summary provides an overview of the three types of autotunnels.
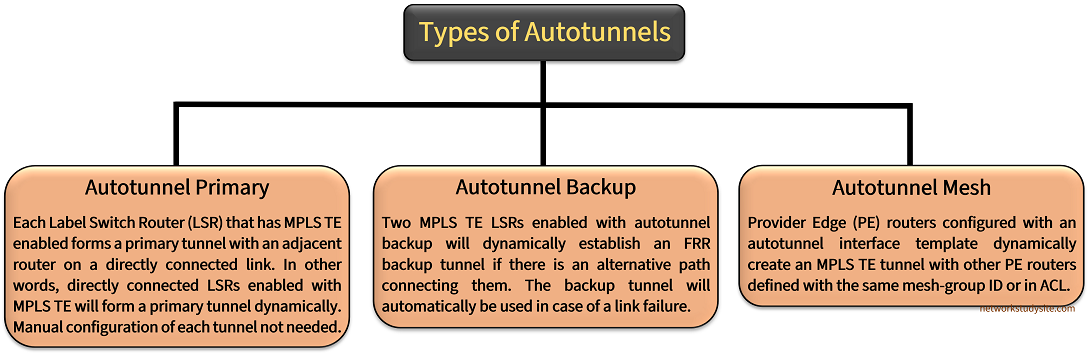
The features described above are listed in the following router output. As visible, each of the autotunnel features has to be enabled separately and the number of created autotunnels can be tracked using the following show command.
R3#show mpls traffic-eng tunnels brief
Signalling Summary:
    LSP Tunnels Process:            running
    Passive LSP Listener:           running
    RSVP Process:                   running
    Forwarding:                     enabled
    auto-tunnel:
        backup Disabled (0 ), id-range:65436-65535          « Autotunnel Backup
        onehop Enabled  (2 ), id-range:50-55                « Autotunnel Primary
        mesh   Disabled (0 ), id-range:64336-65335          « Autotunnel Mesh

    Periodic reoptimization:        every 3600 seconds, next in 1115 seconds
    Periodic FRR Promotion:         Not Running
    Periodic auto-tunnel:
        primary establish scan:     every 10 seconds, next in 5 seconds
        primary rm active scan:     disabled
    Periodic auto-bw collection:    every 300 seconds, next in 215 seconds
TUNNEL NAME                      DESTINATION      UP IF      DOWN IF    STATE/PROT
R3_t50                           4.4.4.4          -         Gi0/1     up/up
R3_t51                           2.2.2.2          -         Gi0/0     up/up
R2_t50                           3.3.3.3          Gi0/0      -          up/up
R4_t50                           3.3.3.3          Gi0/1      -          up/up
Displayed 2 (of 2) heads, 0 (of 0) midpoints, 2 (of 2) tails
Configuring MPLS TE autotunnel primary
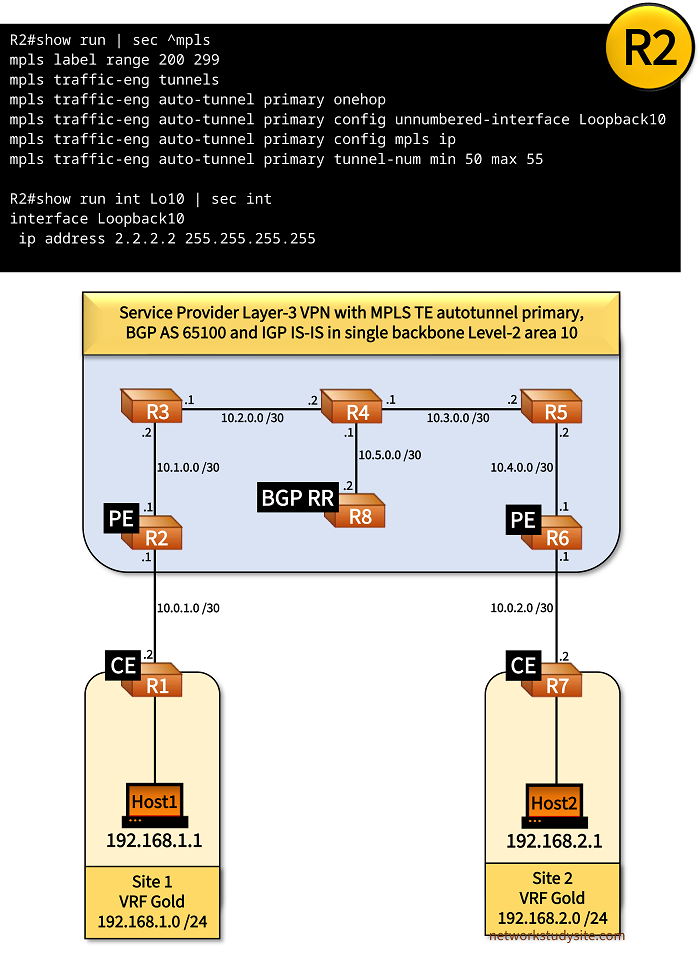
In the following example topology MPLS TE autotunnel primary is configured on each label switching router (LSR) in the Service Provider MPLS L3VPN network. The autotunnel primary feature instructs a router to dynamically create a one-hop tunnel with each of its directly adjacent neighbors that have MPLS TE enabled. In other words, if two directly connected routers have MPLS Traffic Engineering enabled, they will dynamically create a single-hop primary tunnel.
Thus, R2 has an autotunnel with R3, R3 has an autotunnel with R2 and with R4, and so on. To enable a label switched path (LSP) between PE R2 and PE R6 the autotunnels have LDP enabled with the command mpls traffic-eng auto-tunnel primary config mpls ip. As a result, targeted-LDP neighborships are formed between each adjacent LSR to exchange label bindings.
Configuration:
R2 (PE)
R2#show run | sec ^mpls
mpls label range 200 299
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel primary onehop
mpls traffic-eng auto-tunnel primary config unnumbered-interface Loopback10
mpls traffic-eng auto-tunnel primary config mpls ip
mpls traffic-eng auto-tunnel primary tunnel-num min 50 max 55

R2#show run int Lo10 | sec int
interface Loopback10
 ip address 2.2.2.2 255.255.255.255

R2#show run all | sec ^mpls ip__
mpls ip

R2#show run | sec ^vrf
vrf definition Gold
 rd 65100:1
 !
 address-family ipv4
  route-target export 65100:1
  route-target import 65100:2
 exit-address-family

R2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R1 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.1 255.255.255.252

R2#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R3 **
 ip address 10.1.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R2#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0002.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 2.2.2.2
 bgp log-neighbor-changes
 neighbor 8.8.8.8 remote-as 65100
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.1.0 mask 255.255.255.252
  neighbor 10.0.1.2 remote-as 65001
  neighbor 10.0.1.2 activate
 exit-address-family
R6 (PE)
R6#show run | sec ^mpls
mpls label range 600 699
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel primary onehop
mpls traffic-eng auto-tunnel primary config unnumbered-interface Loopback10
mpls traffic-eng auto-tunnel primary config mpls ip
mpls traffic-eng auto-tunnel primary tunnel-num min 50 max 55

R6#show run int Lo10 | sec int
interface Loopback10
 ip address 6.6.6.6 255.255.255.255

R6#show run all | sec ^mpls ip__
mpls ip

R6#show run | sec ^vrf
vrf definition Gold
 rd 65100:2
 !
 address-family ipv4
  route-target export 65100:2
  route-target import 65100:1
 exit-address-family

R6#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R7 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R6#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R7 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.1 255.255.255.252

R6#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.4.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R6#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0006.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 6.6.6.6
 bgp log-neighbor-changes
 neighbor 8.8.8.8 remote-as 65100
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.2.0 mask 255.255.255.252
  neighbor 10.0.2.2 remote-as 65002
  neighbor 10.0.2.2 activate
 exit-address-family
R3
R3#show run | sec ^mpls
mpls label range 300 399
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel primary onehop
mpls traffic-eng auto-tunnel primary config unnumbered-interface Loopback10
mpls traffic-eng auto-tunnel primary config mpls ip
mpls traffic-eng auto-tunnel primary tunnel-num min 50 max 55

R3#show run int Lo10 | sec int
interface Loopback10
 ip address 3.3.3.3 255.255.255.255

R3#show run all | sec ^mpls ip__
mpls ip

R3#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R2 **
 ip address 10.1.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R3#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R4 **
 ip address 10.2.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R3#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0003.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R4
R4#show run | sec ^mpls
mpls label range 400 499
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel primary onehop
mpls traffic-eng auto-tunnel primary config unnumbered-interface Loopback10
mpls traffic-eng auto-tunnel primary config mpls ip
mpls traffic-eng auto-tunnel primary tunnel-num min 50 max 55

R4#show run int Lo10 | sec int
interface Loopback10
 ip address 4.4.4.4 255.255.255.255

R4#show run all | sec ^mpls ip__
mpls ip

R4#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R3 **
 ip address 10.2.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R4#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.3.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R4#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to BGP RR R8 **
 ip address 10.5.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0004.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R5
R5#show run | sec ^mpls
mpls label range 500 599
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel primary onehop
mpls traffic-eng auto-tunnel primary config unnumbered-interface Loopback10
mpls traffic-eng auto-tunnel primary config mpls ip
mpls traffic-eng auto-tunnel primary tunnel-num min 50 max 55

R5#show run int Lo10 | sec int
interface Loopback10
 ip address 5.5.5.5 255.255.255.255

R5#show run all | sec ^mpls ip__
mpls ip

R5#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R6 **
 ip address 10.4.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R5#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R4 **
 ip address 10.3.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R5#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0005.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R8 (BGP RR)
R8#show run int Lo10 | sec int
interface Loopback10
 ip address 8.8.8.8 255.255.255.255

R8#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R4 **
 ip address 10.5.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R8#show run | sec ^router
router isis
 net 49.0010.0000.0000.0008.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 8.8.8.8
 bgp log-neighbor-changes
 neighbor 2.2.2.2 remote-as 65100
 neighbor 2.2.2.2 update-source Loopback10
 neighbor 6.6.6.6 remote-as 65100
 neighbor 6.6.6.6 update-source Loopback10
 !
 address-family vpnv4
  neighbor 2.2.2.2 activate
  neighbor 2.2.2.2 send-community extended
  neighbor 2.2.2.2 route-reflector-client
  neighbor 6.6.6.6 activate
  neighbor 6.6.6.6 send-community extended
  neighbor 6.6.6.6 route-reflector-client
 exit-address-family
R1 (CE)
R1#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Host1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R1#show run int Gi0/0.1 | sec int
interface GigabitEthernet0/0.1
 description ** to Host1 in VRF Gold (VLAN 1) **
 encapsulation dot1Q 1 native
 vrf forwarding Gold
 ip address 192.168.1.2 255.255.255.0

R1#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R1#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.2 255.255.255.252

R1#show run | sec ^router
router bgp 65001
 bgp router-id 1.1.1.1
 bgp log-neighbor-changes
 !
 address-family ipv4 vrf Gold
  network 192.168.1.0
  neighbor 10.0.1.1 remote-as 65100
  neighbor 10.0.1.1 activate
 exit-address-family
R7 (CE)
R7#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R7#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Host2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R7#show run int Gi0/0.1 | sec int
interface GigabitEthernet0/0.1
 description ** to Host2 in VRF Gold (VLAN 1) **
 encapsulation dot1Q 1 native
 vrf forwarding Gold
 ip address 192.168.2.2 255.255.255.0

R7#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R6 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R7#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R6 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.2 255.255.255.252

R7#show run | sec ^router
router bgp 65002
 bgp router-id 7.7.7.7
 bgp log-neighbor-changes
 !
 address-family ipv4 vrf Gold
  network 192.168.2.0
  neighbor 10.0.2.1 remote-as 65100
  neighbor 10.0.2.1 activate
 exit-address-family
Host1
Host1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R1 **
 ip address 192.168.1.1 255.255.255.0
 duplex auto
 speed auto
 media-type rj45

Host1#show run | sec ^ip route
ip route 0.0.0.0 0.0.0.0 192.168.1.2
Host1#ping 192.168.2.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 192.168.2.1, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 48/49/50 ms         « Host1 (Site 1) can reach Host2 (Site 2)


Host1#trace 192.168.2.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.2.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.2 2 msec
  2 10.0.1.1 23 msec
  3 10.1.0.2 [MPLS: Labels 303/606 Exp 0] 48 msec                   « MPLS label stack is used
  4 10.2.0.2 [MPLS: Labels 403/606 Exp 0] 49 msec
  5 10.3.0.2 [MPLS: Labels 503/606 Exp 0] 49 msec
  6 10.0.2.1 [MPLS: Label 606 Exp 0] 28 msec                        « Site 2 VPN Service Label assigned by PE R6
  7 10.0.2.2 48 msec
  8 192.168.2.1 50 msec


R2#show mpls ldp neighbor
    Peer LDP Ident: 3.3.3.3:0; Local LDP Ident 2.2.2.2:0
        TCP connection: 3.3.3.3.21411 - 2.2.2.2.646
        State: Oper; Msgs sent/rcvd: 52/52; Downstream
        Up time: 00:35:47
        LDP discovery sources:
          Targeted Hello 2.2.2.2 -> 3.3.3.3, active, passive        « Targeted-LDP session between PE R2 and R3
        Addresses bound to peer LDP Ident:
          10.1.0.2        10.2.0.1        3.3.3.3


R2#show mpls traffic-eng tunnels brief
Signalling Summary:
    LSP Tunnels Process:            running
    Passive LSP Listener:           running
    RSVP Process:                   running
    Forwarding:                     enabled
    auto-tunnel:
        backup Disabled (0 ), id-range:65436-65535
        onehop Enabled  (1 ), id-range:50-55                        « One primary autotunnel created on PE R2
        mesh   Disabled (0 ), id-range:64336-65335

    Periodic reoptimization:        every 3600 seconds, next in 1365 seconds
    Periodic FRR Promotion:         Not Running
    Periodic auto-tunnel:
        primary establish scan:     every 10 seconds, next in 4 seconds
        primary rm active scan:     disabled
    Periodic auto-bw collection:    every 300 seconds, next in 165 seconds
TUNNEL NAME                      DESTINATION      UP IF      DOWN IF    STATE/PROT
R2_t50                           3.3.3.3          -         Gi0/1     up/up        « TE tunnels are unidirectional, and created in both directions
R3_t51                           2.2.2.2          Gi0/1      -          up/up
Displayed 1 (of 1) heads, 0 (of 0) midpoints, 1 (of 1) tails


R2#show mpls forwarding-table
Local      Outgoing   Prefix           Bytes Label   Outgoing   Next Hop
Label      Label      or Tunnel Id     Switched      interface
200   [T]  Pop Label  3.3.3.3/32       0             Tu50       point2point         « Traffic is forwarding via autotunnel primary
201   [T]  301        4.4.4.4/32       0             Tu50       point2point
202   [T]  302        5.5.5.5/32       0             Tu50       point2point
203   [T]  303        6.6.6.6/32       0             Tu50       point2point
204   [T]  304        8.8.8.8/32       0             Tu50       point2point
205        No Label   10.0.1.0/30[V]   0             aggregate/Gold
206        No Label   192.168.1.0/24[V]   \
                                       2988          Gi0/0.10   10.0.1.2

[T]     Forwarding through a LSP tunnel.
        View additional labelling info with the 'detail' option


R2#show ip int br
Interface                  IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0         unassigned      YES NVRAM  up                    up
GigabitEthernet0/0.10      10.0.1.1        YES NVRAM  up                    up
GigabitEthernet0/1         10.1.0.1        YES NVRAM  up                    up
GigabitEthernet0/2         unassigned      YES NVRAM  administratively down down
GigabitEthernet0/3         unassigned      YES NVRAM  administratively down down
Loopback10                 2.2.2.2         YES NVRAM  up                    up
Tunnel50                   2.2.2.2         YES TFTP   up                    up      « Dynamically created autotunnel primary


R3#show ip int br
Interface                  IP-Address      OK? Method Status                Protocol
GigabitEthernet0/0         10.1.0.2        YES NVRAM  up                    up
GigabitEthernet0/1         10.2.0.1        YES NVRAM  up                    up
GigabitEthernet0/2         unassigned      YES NVRAM  administratively down down
GigabitEthernet0/3         unassigned      YES NVRAM  administratively down down
Loopback10                 3.3.3.3         YES NVRAM  up                    up
Tunnel50                   3.3.3.3         YES TFTP   up                    up
Tunnel51                   3.3.3.3         YES TFTP   up                    up
As visible in the above outputs, Host1 can reach Host2 through a series of autotunnels creating an LSP between the two PE routers. Note that the dynamically created primary autotunnels have Fast Reroute (FRR) enabled by default. In order to benefit from the FRR feature, the autotunnel backup can be configured (which is described in the next section). The following output shows the dynamically created configuration of a primary autotunnel.
R2#show derived-config | sec interface Tunnel50
interface Tunnel50
 ip unnumbered Loopback10
 no logging event link-status
 mpls ip                                                                « LDP enabled
 tunnel mode mpls traffic-eng
 tunnel destination 3.3.3.3
 tunnel mpls traffic-eng autoroute announce
 tunnel mpls traffic-eng path-option 1 explicit name __dynamic_tunnel50
 tunnel mpls traffic-eng fast-reroute                                   « FRR desired, would need additional configuration to enable backup tunnel
 no routing dynamic
In case of a link failure between two LSRs the autotunnel can be dynamically removed. This feature is enabled by adding the example global configuration command mpls traffic-eng auto-tunnel primary timers removal rerouted 60 on R2. As a result, the primary autotunnel state is scanned and verified every 60 seconds on R2, as shown in the following output.
R2#show mpls traffic-eng tunnels brief
Signalling Summary:
    LSP Tunnels Process:            running
    Passive LSP Listener:           running
    RSVP Process:                   running
    Forwarding:                     enabled
    auto-tunnel:
        backup Disabled (0 ), id-range:65436-65535
        onehop Enabled  (1 ), id-range:50-55
        mesh   Disabled (0 ), id-range:64336-65335

    Periodic reoptimization:        every 3600 seconds, next in 172 seconds
    Periodic FRR Promotion:         Not Running
    Periodic auto-tunnel:
        primary establish scan:     every 10 seconds, next in 1 seconds
        primary rm active scan:     every 60 seconds, next in 58 seconds
    Periodic auto-bw collection:    every 300 seconds, next in 172 seconds
TUNNEL NAME                      DESTINATION      UP IF      DOWN IF    STATE/PROT
R2_t50                           3.3.3.3          -         Gi0/1     up/up
R3_t51                           2.2.2.2          Gi0/1      -          up/up
Displayed 1 (of 1) heads, 0 (of 0) midpoints, 1 (of 1) tails
Configuring MPLS TE autotunnel backup
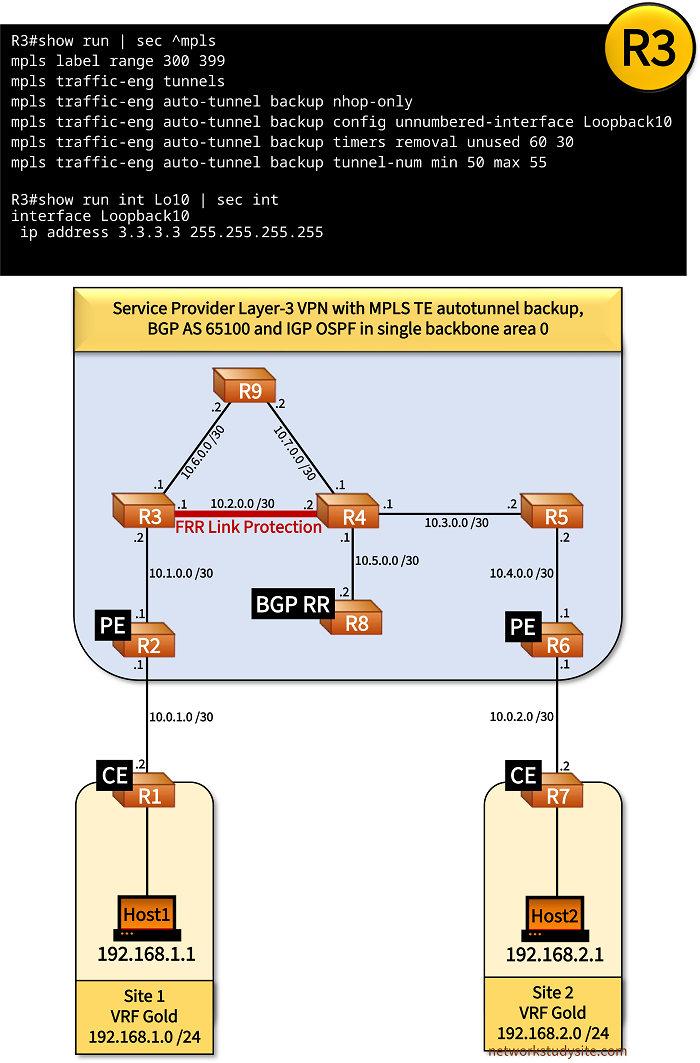
In the following example scenario the link between R3 - R4 is protected with the autotunnel backup feature. This means, the feature is enabled in global configuration mode, instructing the routers to dynamically find and create nhop-only (link protection) fast reroute (FRR) backup tunnels. Since there is an alternative path through R9, the router R3 and R4 establish a backup (bypass) tunnel through the alternative path.
Also, on the protected link BFD is configured for improved failure detection times. When the link fails, traffic is immediately switched to the autotunnel backup path. Note that an additional MPLS label is added for traffic transmitted through the FRR backup tunnel.
Configuration:
R2 (PE)
R2#show run | sec ^mpls
mpls label range 200 299
mpls traffic-eng tunnels

R2#show run | sec ^vrf
vrf definition Gold
 rd 65100:1
 !
 address-family ipv4
  route-target export 65100:1
  route-target import 65100:2
 exit-address-family

R2#show run int Lo10 | sec int
interface Loopback10
 ip address 2.2.2.2 255.255.255.255

R2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R1 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.1 255.255.255.252

R2#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R3 **
 ip address 10.1.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 ip rsvp bandwidth 100 50

R2#show run int Tu10 | sec int
interface Tunnel10
 description ** MPLS TE tunnel to PE R6 **
 ip unnumbered Loopback10
 tunnel mode mpls traffic-eng
 tunnel destination 6.6.6.6
 tunnel mpls traffic-eng autoroute announce
 tunnel mpls traffic-eng priority 1 1
 tunnel mpls traffic-eng bandwidth 50
 tunnel mpls traffic-eng path-option 10 explicit name EXAMPLE-PATH
 tunnel mpls traffic-eng fast-reroute
 no routing dynamic

R2#show run | sec ^ip exp
ip explicit-path name EXAMPLE-PATH enable
 next-address 3.3.3.3
 next-address 4.4.4.4
 next-address 5.5.5.5
 next-address 6.6.6.6

R2#show run | sec ^router
router ospf 10
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng area 0
 router-id 2.2.2.2
 network 2.2.2.2 0.0.0.0 area 0
 network 10.1.0.0 0.0.0.3 area 0
router bgp 65100
 bgp router-id 2.2.2.2
 bgp log-neighbor-changes
 neighbor 8.8.8.8 remote-as 65100
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.1.0 mask 255.255.255.252
  neighbor 10.0.1.2 remote-as 65001
  neighbor 10.0.1.2 activate
 exit-address-family
R6 (PE)
R6#show run | sec ^mpls
mpls label range 600 699
mpls traffic-eng tunnels

R6#show run | sec ^vrf
vrf definition Gold
 rd 65100:2
 !
 address-family ipv4
  route-target export 65100:2
  route-target import 65100:1
 exit-address-family

R6#show run int Lo10 | sec int
interface Loopback10
 ip address 6.6.6.6 255.255.255.255

R6#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R7 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R6#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R7 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.1 255.255.255.252

R6#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.4.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 ip rsvp bandwidth 100 50

R6#show run int Tu10 | sec int
interface Tunnel10
 description ** MPLS TE tunnel to PE R2 **
 ip unnumbered Loopback10
 tunnel mode mpls traffic-eng
 tunnel destination 2.2.2.2
 tunnel mpls traffic-eng autoroute announce
 tunnel mpls traffic-eng priority 1 1
 tunnel mpls traffic-eng bandwidth 50
 tunnel mpls traffic-eng path-option 10 explicit name EXAMPLE-PATH
 tunnel mpls traffic-eng fast-reroute
 no routing dynamic

R6#show run | sec ^ip exp
ip explicit-path name EXAMPLE-PATH enable
 next-address 5.5.5.5
 next-address 4.4.4.4
 next-address 3.3.3.3
 next-address 2.2.2.2

R6#show run | sec ^router
router ospf 10
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng area 0
 router-id 6.6.6.6
 network 6.6.6.6 0.0.0.0 area 0
 network 10.4.0.0 0.0.0.3 area 0
router bgp 65100
 bgp router-id 6.6.6.6
 bgp log-neighbor-changes
 neighbor 8.8.8.8 remote-as 65100
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.2.0 mask 255.255.255.252
  neighbor 10.0.2.2 remote-as 65002
  neighbor 10.0.2.2 activate
 exit-address-family
R3
R3#show run | sec ^mpls
mpls label range 300 399
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel backup nhop-only
mpls traffic-eng auto-tunnel backup config unnumbered-interface Loopback10
mpls traffic-eng auto-tunnel backup timers removal unused 60 30
mpls traffic-eng auto-tunnel backup tunnel-num min 50 max 55

R3#show run int Lo10 | sec int
interface Loopback10
 ip address 3.3.3.3 255.255.255.255

R3#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R2 **
 ip address 10.1.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 ip rsvp bandwidth 100 50

R3#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R4 **
 ip address 10.2.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 bfd interval 100 min_rx 100 multiplier 3
 ip rsvp bandwidth 100 50

R3#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to R9 - autotunnel backup path **
 ip address 10.6.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 ip rsvp bandwidth 100 50

R3#show run | sec ^router
router ospf 10
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng area 0
 router-id 3.3.3.3
 network 3.3.3.3 0.0.0.0 area 0
 network 10.1.0.0 0.0.0.3 area 0
 network 10.2.0.0 0.0.0.3 area 0
 network 10.6.0.0 0.0.0.3 area 0
R4
R4#show run | sec ^mpls
mpls label range 400 499
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel backup nhop-only
mpls traffic-eng auto-tunnel backup config unnumbered-interface Loopback10
mpls traffic-eng auto-tunnel backup timers removal unused 60 30
mpls traffic-eng auto-tunnel backup tunnel-num min 50 max 55

R4#show run int Lo10 | sec int
interface Loopback10
 ip address 4.4.4.4 255.255.255.255

R4#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R3 **
 ip address 10.2.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 bfd interval 100 min_rx 100 multiplier 3
 ip rsvp bandwidth 100 50

R4#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.3.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 ip rsvp bandwidth 100 50

R4#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to BGP RR R8 **
 ip address 10.5.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45

R4#show run int Gi0/3 | sec int
interface GigabitEthernet0/3
 description ** to R9 - autotunnel backup path **
 ip address 10.7.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 ip rsvp bandwidth 100 50

R4#show run | sec ^router
router ospf 10
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng area 0
 router-id 4.4.4.4
 network 4.4.4.4 0.0.0.0 area 0
 network 10.2.0.0 0.0.0.3 area 0
 network 10.3.0.0 0.0.0.3 area 0
 network 10.5.0.0 0.0.0.3 area 0
 network 10.7.0.0 0.0.0.3 area 0
R8 (BGP RR)
R8#show run int Lo10 | sec int
interface Loopback10
 ip address 8.8.8.8 255.255.255.255

R8#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R4 **
 ip address 10.5.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45

R8#show run | sec ^router
router ospf 10
 router-id 8.8.8.8
 network 8.8.8.8 0.0.0.0 area 0
 network 10.5.0.0 0.0.0.3 area 0
router bgp 65100
 bgp router-id 8.8.8.8
 bgp log-neighbor-changes
 neighbor 2.2.2.2 remote-as 65100
 neighbor 2.2.2.2 update-source Loopback10
 neighbor 6.6.6.6 remote-as 65100
 neighbor 6.6.6.6 update-source Loopback10
 !
 address-family vpnv4
  neighbor 2.2.2.2 activate
  neighbor 2.2.2.2 send-community extended
  neighbor 2.2.2.2 route-reflector-client
  neighbor 6.6.6.6 activate
  neighbor 6.6.6.6 send-community extended
  neighbor 6.6.6.6 route-reflector-client
 exit-address-family
R9
R9#show run | sec ^mpls
mpls label range 900 999
mpls traffic-eng tunnels

R9#show run int Lo10 | sec int
interface Loopback10
 ip address 9.9.9.9 255.255.255.255

R9#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R3 **
 ip address 10.6.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 ip rsvp bandwidth 100 50

R9#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R4 **
 ip address 10.7.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 ip rsvp bandwidth 100 50

R9#show run | sec ^router
router ospf 10
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng area 0
 router-id 9.9.9.9
 network 9.9.9.9 0.0.0.0 area 0
 network 10.6.0.0 0.0.0.3 area 0
 network 10.7.0.0 0.0.0.3 area 0
R3#show ip rsvp fast-reroute
Primary                   Protect BW         Backup
Tunnel                    I/F     BPS:Type   Tunnel:Label  State  Level   Type
------                    ------- --------   ------------- ------ -----   ------
** MPLS TE tunnel to PE R Gi0/0   50K:G      None          None   None
** MPLS TE tunnel to PE R Gi0/1   50K:G      Tu52:403      Ready  any-unl Nhop         « Autotunnel backup is ready for use


R3#show mpls traffic-eng tunnels backup
R3_t50
  LSP Head, Tunnel50, Admin: up, Oper: down
  Src 3.3.3.3, Dest 2.2.2.2, Instance 0
  Fast Reroute Backup Provided:
    Protected i/fs: Gi0/0
    Protected lsps: 0 Active lsps: 0
    Backup BW: any pool unlimited; inuse: 0 kbps
R3_t52
  LSP Head, Tunnel52, Admin: up, Oper: up           « Backup tunnel is operational
  Src 3.3.3.3, Dest 4.4.4.4, Instance 1             « Backup tunnel protects LSP between R3 and R4
  Fast Reroute Backup Provided:
    Protected i/fs: Gi0/1
    Protected lsps: 1 Active lsps: 0                « One LSP protected
    Backup BW: any pool unlimited; inuse: 50 kbps


R3#show bfd summary client

Client              Session          Up          Down
FRR                       1           1             0      « Fast Reroute is a client of BFD
CEF                       1           1             0

Total                     1           1             0


Host1#trace 192.168.2.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.2.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.2 2 msec
  2 10.0.1.1 24 msec
  3 10.1.0.2 [MPLS: Labels 304/606 Exp 0] 70 msec          « LSP before link failure
  4 10.2.0.2 [MPLS: Labels 403/606 Exp 0] 71 msec
  5 10.3.0.2 [MPLS: Labels 503/606 Exp 0] 72 msec
  6 10.0.2.1 [MPLS: Label 606 Exp 0] 49 msec
  7 10.0.2.2 70 msec
  8 192.168.2.1 72 msec


Host1#ping 192.168.2.1 re 100
Type escape sequence to abort.
Sending 100, 100-byte ICMP Echos to 192.168.2.1, timeout is 2 seconds:
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!.!!!!!!!!!!!!!
!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!
Success rate is 99 percent (99/100), round-trip min/avg/max = 68/79/96 ms       « Link failure causes single packet loss


Host1#trace 192.168.2.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.2.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.2 2 msec
  2 10.0.1.1 24 msec
  3 10.1.0.2 [MPLS: Labels 304/606 Exp 0] 92 msec
  4 10.6.0.2 [MPLS: Labels 900/403/606 Exp 0] 94 msec      « Additional MPLS label added for traffic in backup tunnel
  5 10.7.0.1 [MPLS: Labels 403/606 Exp 0] 92 msec
  6 10.3.0.2 [MPLS: Labels 503/606 Exp 0] 92 msec
  7 10.0.2.1 [MPLS: Label 606 Exp 0] 71 msec
  8 10.0.2.2 92 msec
  9 192.168.2.1 91 msec
Configuring MPLS TE autotunnel mesh
In the following example scenario the two PE routers establish an LSP across the Service Provider network using an MPLS TE tunnel template. This means, a tunnel interface template is configured (similar to DVTI), and the template configuration is cloned to any number of automatically created MPLS TE tunnels.
The tunnel peers are configured with either an access-list (ACL) or using a mesh group. Note the routing protocol IS-IS only supports ACLs with autotunnel mesh. Therefore, in the following example an ACL is used on each PE router to identify any other PE routers within the autotunnel mesh network. The PEs allowed by the ACL will automatically establish an MPLS TE tunnel based on the template, and create an LSP.
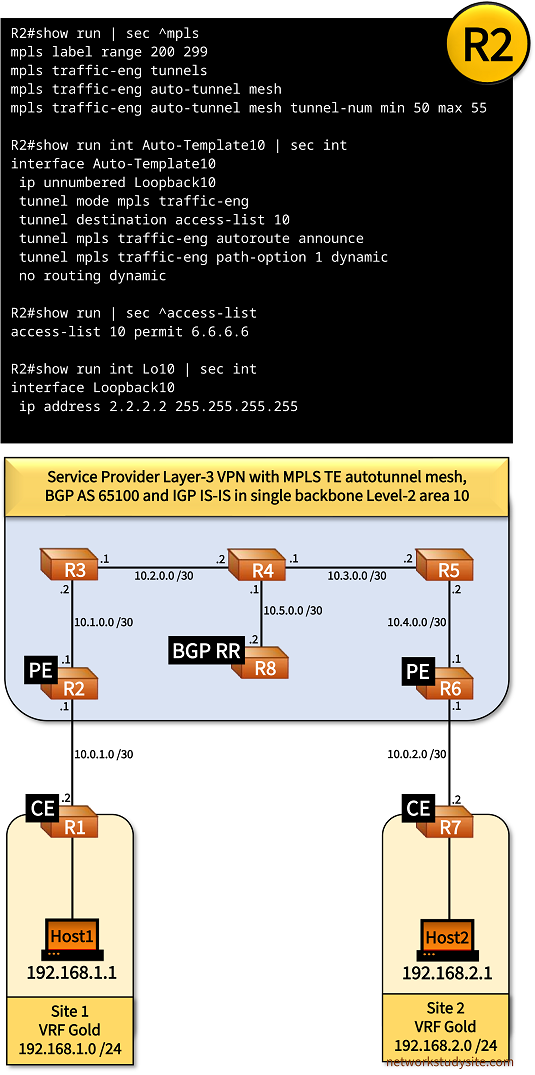
Configuration:
R2 (PE)
R2#show run | sec ^mpls
mpls label range 200 299
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel mesh
mpls traffic-eng auto-tunnel mesh tunnel-num min 50 max 55

R2#show run int Auto-Template10 | sec int
interface Auto-Template10
 ip unnumbered Loopback10
 tunnel mode mpls traffic-eng
 tunnel destination access-list 10
 tunnel mpls traffic-eng autoroute announce
 tunnel mpls traffic-eng path-option 1 dynamic
 no routing dynamic

R2#show run | sec ^access-list
access-list 10 permit 6.6.6.6

R2#show run int Lo10 | sec int
interface Loopback10
 ip address 2.2.2.2 255.255.255.255

R2#show run | sec ^vrf
vrf definition Gold
 rd 65100:1
 !
 address-family ipv4
  route-target export 65100:1
  route-target import 65100:2
 exit-address-family

R2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R1 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.1 255.255.255.252

R2#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R3 **
 ip address 10.1.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R2#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0002.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 2.2.2.2
 bgp log-neighbor-changes
 neighbor 8.8.8.8 remote-as 65100
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.1.0 mask 255.255.255.252
  neighbor 10.0.1.2 remote-as 65001
  neighbor 10.0.1.2 activate
 exit-address-family
R6 (PE)
R6#show run | sec ^mpls
mpls label range 600 699
mpls traffic-eng tunnels
mpls traffic-eng auto-tunnel mesh
mpls traffic-eng auto-tunnel mesh tunnel-num min 50 max 55

R6#show run int Auto-Template10 | sec int
interface Auto-Template10
 ip unnumbered Loopback10
 tunnel mode mpls traffic-eng
 tunnel destination access-list 10
 tunnel mpls traffic-eng autoroute announce
 tunnel mpls traffic-eng path-option 1 dynamic
 no routing dynamic

R6#show run | sec ^access-list
access-list 10 permit 2.2.2.2

R6#show run int Lo10 | sec int
interface Loopback10
 ip address 6.6.6.6 255.255.255.255

R6#show run | sec ^vrf
vrf definition Gold
 rd 65100:2
 !
 address-family ipv4
  route-target export 65100:2
  route-target import 65100:1
 exit-address-family

R6#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R7 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R6#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R7 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.1 255.255.255.252

R6#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.4.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R6#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0006.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65100
 bgp router-id 6.6.6.6
 bgp log-neighbor-changes
 neighbor 8.8.8.8 remote-as 65100
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.2.0 mask 255.255.255.252
  neighbor 10.0.2.2 remote-as 65002
  neighbor 10.0.2.2 activate
 exit-address-family
R3
R3#show run | sec ^mpls
mpls label range 300 399
mpls traffic-eng tunnels

R3#show run int Lo10 | sec int
interface Loopback10
 ip address 3.3.3.3 255.255.255.255

R3#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R2 **
 ip address 10.1.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R3#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R4 **
 ip address 10.2.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R3#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0003.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R4
R4#show run | sec ^mpls
mpls label range 400 499
mpls traffic-eng tunnels

R4#show run int Lo10 | sec int
interface Loopback10
 ip address 4.4.4.4 255.255.255.255

R4#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R3 **
 ip address 10.2.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R4#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to R5 **
 ip address 10.3.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls traffic-eng tunnels
 isis circuit-type level-2-only
 isis network point-to-point
 ip rsvp bandwidth 100 50

R4#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to BGP RR R8 **
 ip address 10.5.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run | sec ^router
router isis
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng level-2
 net 49.0010.0000.0000.0004.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R2#show mpls traffic-eng auto-tunnel mesh

Auto-Template10:

 Using access-list 10 to clone the following tunnel interfaces:

  Destination         Interface
  -----------         ---------

  6.6.6.6             Tunnel50             « Tunnel automatically created

Mesh tunnel interface numbers: min 50 max 55


R2#show mpls traffic-eng tunnels brief
Signalling Summary:
    LSP Tunnels Process:            running
    Passive LSP Listener:           running
    RSVP Process:                   running
    Forwarding:                     enabled
    auto-tunnel:
        backup Disabled (0 ), id-range:65436-65535
        onehop Disabled (0 ), id-range:65336-65435
        mesh   Enabled  (1 ), id-range:50-55            « Autotunnel mesh is enabled

    Periodic reoptimization:        every 3600 seconds, next in 3428 seconds
    Periodic FRR Promotion:         Not Running
    Periodic auto-bw collection:    every 300 seconds, next in 128 seconds
TUNNEL NAME                      DESTINATION      UP IF      DOWN IF    STATE/PROT
R2_t50                           6.6.6.6          -         Gi0/1     up/up              « This is the tunnel head
R6_t50                           2.2.2.2          Gi0/1      -          up/up            « This is the tunnel tail
Displayed 1 (of 1) heads, 0 (of 0) midpoints, 1 (of 1) tails


Host1#trace 192.168.2.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.2.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.2 2 msec
  2 10.0.1.1 23 msec
  3 10.1.0.2 [MPLS: Labels 300/606 Exp 0] 48 msec              « MPLS label switching is used
  4 10.2.0.2 [MPLS: Labels 401/606 Exp 0] 50 msec
  5 10.3.0.2 [MPLS: Labels 501/606 Exp 0] 48 msec
  6 10.0.2.1 [MPLS: Label 606 Exp 0] 26 msec
  7 10.0.2.2 49 msec
  8 192.168.2.1 50 msec
In the following outputs the same network is recreated using OSPF as the IGP, instead of IS-IS. The displayed configuration is taken from the PE router R2 and R6, and shows the MPLS TE autotunnel mesh-group being used to identify each PE router in the network.
R2#show run | sec ^router ospf
router ospf 10
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng area 0
 mpls traffic-eng mesh-group 10 Loopback10 area 0           « The mesh-group ID 10 is used between the PE routers
 router-id 2.2.2.2
 network 2.2.2.2 0.0.0.0 area 0
 network 10.1.0.0 0.0.0.3 area 0


-----------------------------------------------------


R6#show run | sec ^router ospf
router ospf 10
 mpls traffic-eng router-id Loopback10
 mpls traffic-eng area 0
 mpls traffic-eng mesh-group 10 Loopback10 area 0
 router-id 6.6.6.6
 network 6.6.6.6 0.0.0.0 area 0
 network 10.4.0.0 0.0.0.3 area 0
The following outputs are taken from the PE router R2 showing the mesh-group ID 10 advertised by the OSPF routing protocol. This feature is available only with OSPF, and is not available with IS-IS.
R2#show mpls traffic-eng topology area 0 igp-id ospf 6.6.6.6 brief

IGP Id: 6.6.6.6, MPLS TE Id:6.6.6.6 Router Node  (ospf 10  area 0)
Area mg-id's:
: mg-id 10    6.6.6.6 :                                « Mesh-group ID 10
      link[0]: Point-to-Point, Nbr IGP Id: 5.5.5.5, nbr_node_id:10, gen:14
          frag_id 2, Intf Address:10.4.0.1, Nbr Intf Address:10.4.0.2
          TE metric:1, IGP metric:1, attribute flags:0x0
          SRLGs: None


R2#show ip ospf database opaque-area adv-router 6.6.6.6 | beg Number of Links : 1
    Number of Links : 1

  LS age: 655
  Options: (No TOS-capability, DC)
  LS Type: Opaque Area Link
  Link State ID: 4.0.0.0
  Opaque Type: 4 (Router Information)
  Opaque ID: 0
  Advertising Router: 6.6.6.6
  LS Seq Number: 80000002
  Checksum: 0xD893
  Length: 40

    TLV Type: Router Information
    Length: 4
    Capabilities:
      Graceful Restart Helper
      Stub Router Support
      Traffic Engineering Support

    TLV Type: Mesh-group (IPv4)                        « Mesh-group information carried in OSPF Opaque LSA
    Length: 8
    Encoding: Cisco
      Mesh-group Number: 10
        Tail-end IP: 6.6.6.6
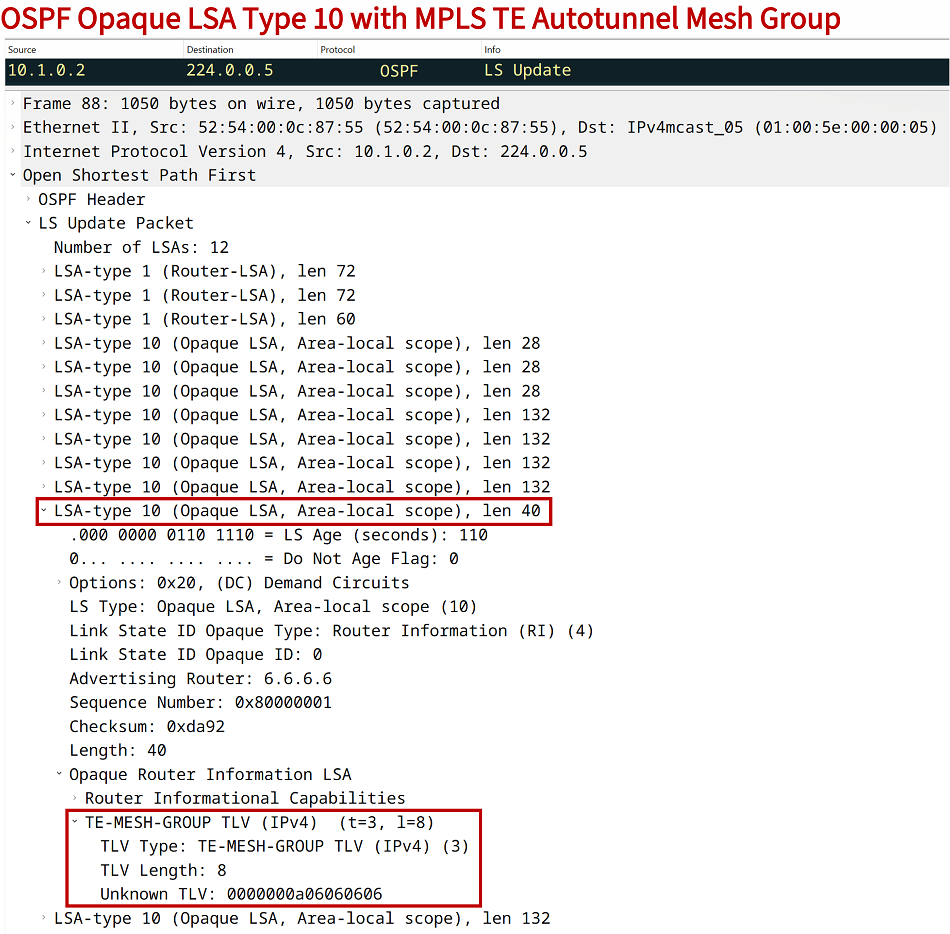
The details shown in the router outputs taken from the OSPF database are displayed in the following packet capture. As visible, OSPF uses the Opaque LSA Type 10 to distribute information regarding the MPLS Traffic Engineering Autotunnel Mesh Group. With this integrated feature, PE routers can use the mesh-group ID to indentify each other and dynamically establish MPLS TE tunnels.