Inter-AS Option A Tutorial with MPLS L3VPN Configuration
Table of Contents
- What is MPLS inter-AS option A? ‹
- Inter-AS option A network design choices ‹
- How to configure MPLS inter-AS option A? ‹
- Download section ‹
What is MPLS inter-AS option A?
Inter-AS option A extends an MPLS L3VPN between two Service Provider Autonomous Systems through directly connected VRF-aware subinterfaces. The inter-AS interconnection is not label switched and the directly connected ASBR Provider Edge (PE) routers have at least one subinterface for each customer. The ASBR PEs share unlabeled IP prefixes with each other through the dedicated customer VRFs.
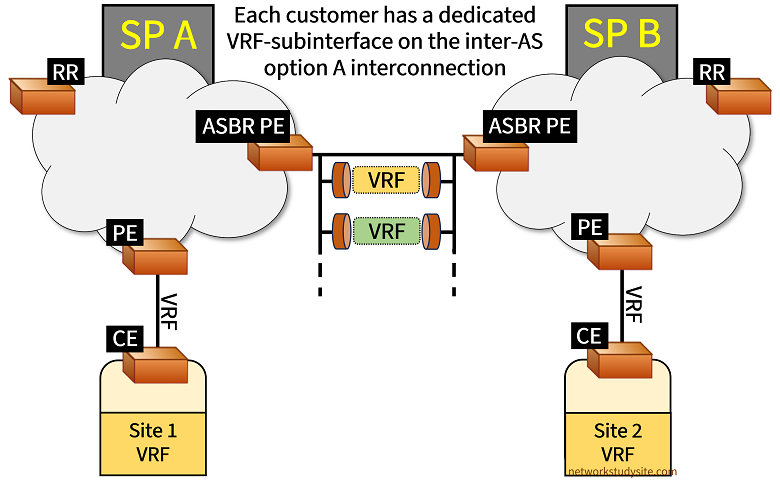
This solution has a low level of complexity but does not scale well because each customer VPN requires its own VRF-subinterface on the ASBR PEs. Regarding QoS the inter-AS link can use the IP DSCP field and a service policy configured per each VRF-subinterface. This is important because most MPLS L3VPN solutions guarantee end-to-end QoS SLAs betwen subscriber locations.
Inter-AS option A network design choices
A variety of deployments are possible with inter-AS options A listed in the following table.
| Design option | Description |
|---|---|
| Inter-AS customer locations have same BGP AS Number | If the PE-CE routing protocol is BGP, then two inter-AS connected customer locations may have the same BGP ASN assigned. In such a scenario the CE routers need to be instructed to accept BGP updates with the same ASN in the AS Path. |
| The ASBR PE to PE uses EIGRP or OSPF | The interconnection between the two Service Providers can use a variety of dynamic routing protocols to distribute the inter-AS IP prefixes. Essentially this link is treated as a PE-CE connection by each ASBR PE. The chosen routing protocol can influence whether the customer location receives IGP routes as internal or external. |
How to configure MPLS inter-AS option A?
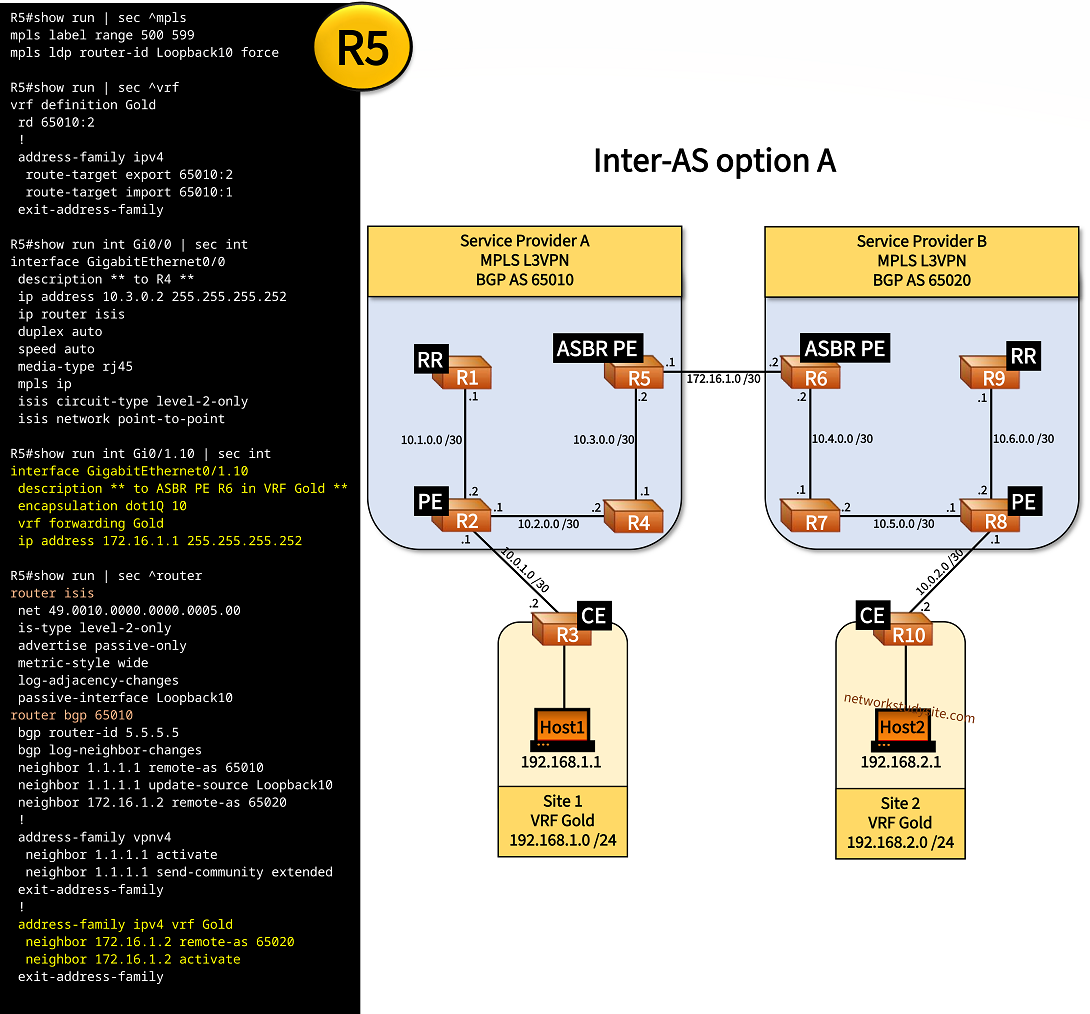
In the following example topology two sites of the same customer are connected with two different MPLS L3VPN Service Providers. By configuring inter-AS option A, the two sites can use MPLS label switching to reach each other. Note that with inter-as option A there is no end-to-end Label Switched Path (LSP) between the PE router R2 and the PE R8 because the inter-AS interconnection is not label switched.
The inter-AS interconnection is configured between the ASBR PE routers R5 and PE R6 using IP forwarding on directly connected VRF-aware subinterfaces assigned to the customer's VRF (VRF Gold). The ASBR PE routers act as regular PE routers by having a Multiprotocol-BGP neighborship with a Route Reflector (RR) and exchanging Route Distinguisher and Route Target values with VPNv4 prefixes. In this example scenario the ASBR PE routers establish an eBGP neighborship with each other.
Configuration:
R5 (ASBR PE)
R5#show run all | sec ^mpls ip__
mpls ip

R5#show run | sec ^mpls
mpls label range 500 599
mpls ldp router-id Loopback10 force

R5#show run | sec ^vrf
vrf definition Gold
 rd 65010:2
 !
 address-family ipv4
  route-target export 65010:2
  route-target import 65010:1
 exit-address-family

R5#show run int Lo10 | sec int
interface Loopback10
 ip address 5.5.5.5 255.255.255.255

R5#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R4 **
 ip address 10.3.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ASBR PE R6 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R5#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to ASBR PE R6 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 172.16.1.1 255.255.255.252

R5#show run | sec ^router
router isis
 net 49.0010.0000.0000.0005.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 5.5.5.5
 bgp log-neighbor-changes
 neighbor 1.1.1.1 remote-as 65010
 neighbor 1.1.1.1 update-source Loopback10
 neighbor 172.16.1.2 remote-as 65020
 !
 address-family vpnv4
  neighbor 1.1.1.1 activate
  neighbor 1.1.1.1 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  neighbor 172.16.1.2 remote-as 65020
  neighbor 172.16.1.2 activate
 exit-address-family
R6 (ASBR PE)
R6#show run all | sec ^mpls ip__
mpls ip

R6#show run | sec ^mpls
mpls label range 600 699
mpls ldp router-id Loopback10 force

R6#show run | sec ^vrf
vrf definition Gold
 rd 65020:2
 !
 address-family ipv4
  route-target export 65020:2
  route-target import 65020:1
 exit-address-family

R6#show run int Lo10 | sec int
interface Loopback10
 ip address 6.6.6.6 255.255.255.255

R6#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R7 **
 ip address 10.4.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls ip

R6#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ASBR PE R5 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R6#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to ASBR PE R5 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 172.16.1.2 255.255.255.252

R6#show run | sec ^router
router ospf 10
 router-id 6.6.6.6
 network 6.6.6.6 0.0.0.0 area 0
 network 10.4.0.0 0.0.0.3 area 0
router bgp 65020
 bgp router-id 6.6.6.6
 bgp log-neighbor-changes
 neighbor 9.9.9.9 remote-as 65020
 neighbor 9.9.9.9 update-source Loopback10
 !
 address-family vpnv4
  neighbor 9.9.9.9 activate
  neighbor 9.9.9.9 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  neighbor 172.16.1.1 remote-as 65010
  neighbor 172.16.1.1 activate
 exit-address-family
R1 (RR)
R1#show run int Lo10 | sec int
interface Loopback10
 ip address 1.1.1.1 255.255.255.255

R1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R2 **
 ip address 10.1.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R1#show run | sec ^router
router isis
 net 49.0010.0000.0000.0001.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 1.1.1.1
 bgp log-neighbor-changes
 neighbor 2.2.2.2 remote-as 65010
 neighbor 2.2.2.2 update-source Loopback10
 neighbor 5.5.5.5 remote-as 65010
 neighbor 5.5.5.5 update-source Loopback10
 !
 address-family vpnv4
  neighbor 2.2.2.2 activate
  neighbor 2.2.2.2 send-community extended
  neighbor 2.2.2.2 route-reflector-client
  neighbor 5.5.5.5 activate
  neighbor 5.5.5.5 send-community extended
  neighbor 5.5.5.5 route-reflector-client
 exit-address-family
R9 (RR)
R9#show run int Lo10 | sec int
interface Loopback10
 ip address 9.9.9.9 255.255.255.255

R9#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R8 **
 ip address 10.6.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45

R9#show run | sec ^router
router ospf 10
 router-id 9.9.9.9
 network 9.9.9.9 0.0.0.0 area 0
 network 10.6.0.0 0.0.0.3 area 0
router bgp 65020
 bgp router-id 9.9.9.9
 bgp log-neighbor-changes
 neighbor 6.6.6.6 remote-as 65020
 neighbor 6.6.6.6 update-source Loopback10
 neighbor 8.8.8.8 remote-as 65020
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 6.6.6.6 activate
  neighbor 6.6.6.6 send-community extended
  neighbor 6.6.6.6 route-reflector-client
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
  neighbor 8.8.8.8 route-reflector-client
 exit-address-family
R2 (PE)
R2#show run all | sec ^mpls ip__
mpls ip

R2#show run | sec ^mpls
mpls label range 200 299
mpls ldp router-id Loopback10 force

R2#show run | sec ^vrf
vrf definition Gold
 rd 65010:1
 !
 address-family ipv4
  route-target export 65010:1
  route-target import 65010:2
 exit-address-family

R2#show run int Lo10 | sec int
interface Loopback10
 ip address 2.2.2.2 255.255.255.255

R2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R3 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R3 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.1 255.255.255.252

R2#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to RR R1 **
 ip address 10.1.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R2#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to R4 **
 ip address 10.2.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R2#show run | sec ^router
router isis
 net 49.0010.0000.0000.0002.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 2.2.2.2
 bgp log-neighbor-changes
 neighbor 1.1.1.1 remote-as 65010
 neighbor 1.1.1.1 update-source Loopback10
 !
 address-family vpnv4
  neighbor 1.1.1.1 activate
  neighbor 1.1.1.1 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.1.0 mask 255.255.255.252
  neighbor 10.0.1.2 remote-as 65001
  neighbor 10.0.1.2 activate
 exit-address-family
R8 (PE)
R8#show run all | sec ^mpls ip__
mpls ip

R8#show run | sec ^mpls
mpls label range 800 899
mpls ldp router-id Loopback10 force

R8#show run | sec ^vrf
vrf definition Gold
 rd 65020:1
 !
 address-family ipv4
  route-target export 65020:1
  route-target import 65020:2
 exit-address-family

R8#show run int Lo10 | sec int
interface Loopback10
 ip address 8.8.8.8 255.255.255.255

R8#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R10 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R8#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R10 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.1 255.255.255.252

R8#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to RR R9 **
 ip address 10.6.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45

R8#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to R7 **
 ip address 10.5.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls ip

R8#show run | sec ^router
router ospf 10
 router-id 8.8.8.8
 network 8.8.8.8 0.0.0.0 area 0
 network 10.5.0.0 0.0.0.3 area 0
 network 10.6.0.0 0.0.0.3 area 0
router bgp 65020
 bgp router-id 8.8.8.8
 bgp log-neighbor-changes
 neighbor 9.9.9.9 remote-as 65020
 neighbor 9.9.9.9 update-source Loopback10
 !
 address-family vpnv4
  neighbor 9.9.9.9 activate
  neighbor 9.9.9.9 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.2.0 mask 255.255.255.252
  neighbor 10.0.2.2 remote-as 65002
  neighbor 10.0.2.2 activate
 exit-address-family
R4
R4#show run all | sec ^mpls ip__
mpls ip

R4#show run | sec ^mpls
mpls label range 400 499
mpls ldp router-id Loopback10 force

R4#show run int Lo10 | sec int
interface Loopback10
 ip address 4.4.4.4 255.255.255.255

R4#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R2 **
 ip address 10.2.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ASBR PE R5 **
 ip address 10.3.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run | sec ^router
router isis
 net 49.0010.0000.0000.0004.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R7
R7#show run all | sec ^mpls ip__
mpls ip

R7#show run | sec ^mpls
mpls label range 700 799
mpls ldp router-id Loopback10 force

R7#show run int Lo10 | sec int
interface Loopback10
 ip address 7.7.7.7 255.255.255.255

R7#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R8 **
 ip address 10.5.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls ip

R7#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ASBR PE R6 **
 ip address 10.4.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls ip

R7#show run | sec ^router
router ospf 10
 router-id 7.7.7.7
 network 7.7.7.7 0.0.0.0 area 0
 network 10.4.0.0 0.0.0.3 area 0
 network 10.5.0.0 0.0.0.3 area 0
R3 (CE)
R3#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R3#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Host1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R3#show run int Gi0/0.1 | sec int
interface GigabitEthernet0/0.1
 description ** to Host1 in VRF Gold (VLAN 1) **
 encapsulation dot1Q 1 native
 vrf forwarding Gold
 ip address 192.168.1.2 255.255.255.0

R3#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R3#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.2 255.255.255.252

R3#show run | sec ^router
router bgp 65001
 bgp router-id 3.3.3.3
 bgp log-neighbor-changes
 !
 address-family ipv4 vrf Gold
  network 192.168.1.0
  neighbor 10.0.1.1 remote-as 65010
  neighbor 10.0.1.1 activate
 exit-address-family
R10 (CE)
R10#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R10#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Host2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R10#show run int Gi0/0.1 | sec int
interface GigabitEthernet0/0.1
 description ** to Host2 in VRF Gold (VLAN 1) **
 encapsulation dot1Q 1 native
 vrf forwarding Gold
 ip address 192.168.2.2 255.255.255.0

R10#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R8 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R10#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R8 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.2 255.255.255.252

R10#show run | sec ^router
router bgp 65002
 bgp router-id 10.10.10.10
 bgp log-neighbor-changes
 !
 address-family ipv4 vrf Gold
  network 192.168.2.0
  neighbor 10.0.2.1 remote-as 65020
  neighbor 10.0.2.1 activate
 exit-address-family
Host1
Host1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R3 **
 ip address 192.168.1.1 255.255.255.0
 duplex auto
 speed auto
 media-type rj45

Host1#show run | sec ^ip route
ip route 0.0.0.0 0.0.0.0 192.168.1.2
Host2
Host2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R10 **
 ip address 192.168.2.1 255.255.255.0
 duplex auto
 speed auto
 media-type rj45

Host2#show run | sec ^ip route
ip route 0.0.0.0 0.0.0.0 192.168.2.2
Host1#trace 192.168.2.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.2.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.2 2 msec
  2 10.0.1.1 24 msec
  3 10.2.0.2 [MPLS: Labels 400/504 Exp 0] 46 msec
  4 172.16.1.1 [MPLS: Label 504 Exp 0] 25 msec
  5 172.16.1.2 47 msec                              « Inter-AS interconnection is not label switched
  6 10.4.0.1 [MPLS: Labels 702/805 Exp 0] 70 msec
  7 10.0.2.1 [MPLS: Label 805 Exp 0] 48 msec
  8 10.0.2.2 70 msec
  9 192.168.2.1 71 msec


Host1#ping 192.168.2.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 192.168.2.1, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 69/70/76 ms       « Host1 can ping Host2 due to inter-AS option A


Host2#trace 192.168.1.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.1.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.2.2 1 msec
  2 10.0.2.1 24 msec
  3 10.5.0.2 [MPLS: Labels 700/606 Exp 0] 47 msec                   « To reach remote prefix, path to local ASBR is label switched
  4 172.16.1.2 [MPLS: Label 606 Exp 0] 24 msec
  5 172.16.1.1 47 msec
  6 10.3.0.1 [MPLS: Labels 401/204 Exp 0] 69 msec
  7 10.0.1.1 [MPLS: Label 204 Exp 0] 48 msec
  8 10.0.1.2 69 msec
  9 192.168.1.1 71 msec


Host2#ping 192.168.1.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 192.168.1.1, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 70/71/73 ms
The label range is configured on each MPLS router, this means R2 uses the range 200 - 299, R5 uses 500 - 599 and so on. As visible in the above traceroute, the ASBR PE R6 assigns the VPN label 606 for traffic destined to reach the other/remote Service Provider.
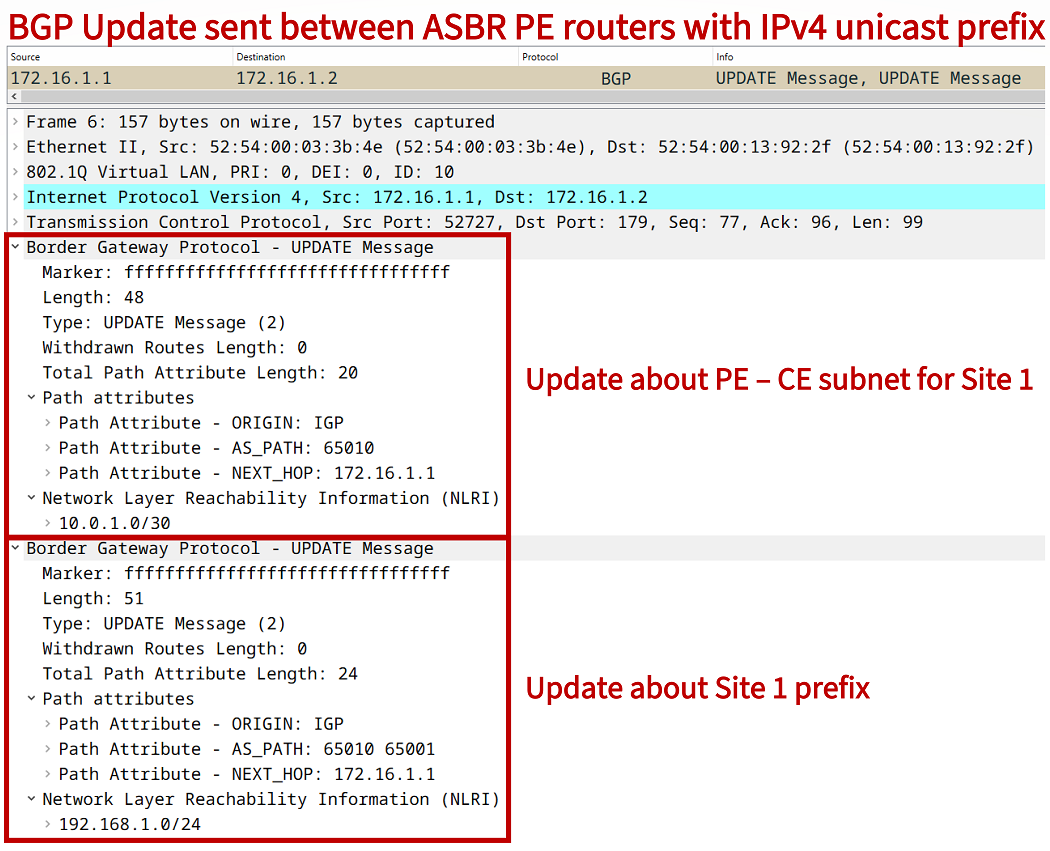
However, the inter-AS connection is not label switched as shown in the following packet capture taken between ASBR PE routers. Notably, the BGP Update message sent between ASBR PE routers advertises IPv4 unicast prefixes which do not have MPLS labels assigned.
R6#show ip bgp vpnv4 vrf Gold 192.168.1.0
BGP routing table entry for 65020:2:192.168.1.0/24, version 3
Paths: (1 available, best #1, table Gold)
  Advertised to update-groups:
     2
  Refresh Epoch 1
  65010 65001
    172.16.1.1 (via vrf Gold) from 172.16.1.1 (5.5.5.5)
      Origin IGP, localpref 100, valid, external, best
      Extended Community: RT:65020:2
      mpls labels in/out 606/nolabel                   « No label attached to reach inter-AS remote prefix 192.168.1.0/24 from ASBR PE R6
      rx pathid: 0, tx pathid: 0x0


R6#show mpls forwarding-table
Local      Outgoing   Prefix           Bytes Label   Outgoing   Next Hop
Label      Label      or Tunnel Id     Switched      interface
600        Pop Label  7.7.7.7/32       0             Gi0/0      10.4.0.1
601        Pop Label  10.5.0.0/30      0             Gi0/0      10.4.0.1
602        701        8.8.8.8/32       0             Gi0/0      10.4.0.1
603        702        10.6.0.0/30      0             Gi0/0      10.4.0.1
604        703        9.9.9.9/32       0             Gi0/0      10.4.0.1
605        No Label   10.0.1.0/30[V]   0             Gi0/1.10   172.16.1.1
606        No Label   192.168.1.0/24[V]   \                                      « Inter-AS link does not have label attached
                                       10554         Gi0/1.10   172.16.1.1


R6#show mpls forwarding-table vrf Gold 192.168.1.0 detail
Local      Outgoing   Prefix           Bytes Label   Outgoing   Next Hop
Label      Label      or Tunnel Id     Switched      interface
606        No Label   192.168.1.0/24[V]   \
                                       10554         Gi0/1.10   172.16.1.1
        MAC/Encaps=18/18, MRU=1504, Label Stack{}                                        « Label stack is empty for prefix from Inter-AS neighbor
        525400033B4E52540013922F8100000A0800
        VPN route: Gold                                                                  « Prefix is received in dedicated customer VRF Gold
        No output feature configured


R6#show ip cef vrf Gold 192.168.1.0 detail
192.168.1.0/24, epoch 0, flags [rib only nolabel, rib defined all labels]
  dflt local label info: other/606 [0x2]
  recursive via 172.16.1.1
    attached to GigabitEthernet0/1.10
Once an inter-AS prefix enters a local AS, the ASBR PE router assigns a label stack to it. In other words, the path between the PE R2 and ASBR PE R5 is label switched (also visible in traceroutes). The following outputs show the Route Reflector R1 and PE R2 receiving BGP Updates about the remote inter-AS prefix for Site 2. The ASBR PE R5 has attached its own label 504 to this remote prefix.
R1#show ip bgp vpnv4 all 192.168.2.0
BGP routing table entry for 65010:2:192.168.2.0/24, version 5         « Site2 VPNv4 prefix received on RR R1
Paths: (1 available, best #1, no table)
Flag: 0x100
  Advertised to update-groups:
     1
  Refresh Epoch 1
  65020 65002, (Received from a RR-client)                            « AS Path assigned to the Site 2 prefix
    5.5.5.5 (metric 30) (via default) from 5.5.5.5 (5.5.5.5)
      Origin IGP, metric 0, localpref 100, valid, internal, best
      Extended Community: RT:65010:2                                  « Route Target value assigned by ASBR PE R5
      mpls labels in/out nolabel/504                                  « ASBR PE R5 assigned VPN service label 504
      rx pathid: 0, tx pathid: 0x0


R2#show ip bgp vpnv4 rd 65010:2 192.168.2.0
BGP routing table entry for 65010:2:192.168.2.0/24, version 5
Paths: (1 available, best #1, no table)
Flag: 0x100
  Not advertised to any peer
  Refresh Epoch 1
  65020 6500
    5.5.5.5 (metric 20) (via default) from 1.1.1.1 (1.1.1.1)
      Origin IGP, metric 0, localpref 100, valid, internal, best
      Extended Community: RT:65010:2
      Originator: 5.5.5.5, Cluster list: 1.1.1.1                      « PE router R2 receives the Site2 VPNv4 prefix originated by ASBR PE R5
      mpls labels in/out nolabel/504
      rx pathid: 0, tx pathid: 0x0