Inter-AS Option B Configuration with MPLS L3VPN Explained
Table of Contents
- What is MPLS inter-AS option B? ‹
- Inter-AS option B network design choices ‹
- How to configure MPLS inter-AS option B? ‹
- Download section ‹
What is MPLS inter-AS option B?
Inter-AS option B is a method to interconnect two MPLS L3VPN networks using a single label switched interface on the ASBR Provider Edge (PE) routers. On the ASBR PE routers there are no VRF subinterfaces and no VRFs configured. The ASBR PEs act like inline BGP Route Reflectors because they redistribute BGP VPNv4 prefixes and also forward label switched traffic between two MPLS networks.

Inter-AS option B is more scalable and easier to manage than option A. This is because there are no VRF subinterfaces needed for each customer on the inter-AS option B interconnection. In fact, VRFs do not need to be configured at all on the ASBR PEs. Another advantage of inter-AS option B is the end-to-end label switched path (LSP) between the PE routers.
Inter-AS option B network design choices
Inter-AS option B allows for a variety of design options which are listed in the following table.
| Design option | Description |
|---|---|
| To keep or instead to rewrite the received Route Target value on the ASBR PE routers | The ASBR PE receives the Route Target (RT) value unchanged from the neighboring ASBR PE. It may cause issues if the RT value of the other Service Provider's network is inserted into the local MPLS L3VPN. As a solution, the ASBR PE is configured to rewrite (change) the RT value before advertising inter-AS VPNv4 prefixes to the local RR. The option to rewrite the RT is shown in this blog post's next section. |
| To configure iBGP next-hop-self on the ASBR PE or instead to redistribute connected inter-AS subnet into local MPLS IGP | The inter-AS link between the two Service Providers uses a single eBGP neighborship on a directly connected label switching interface. This means, the ASBR PE router needs to use the next-hop-self feature towards its local iBGP Route Reflector when advertising inter-AS BGP VPNv4 routes. Or alternatively, the ASBR PE can redistribute the inter-AS link's subnet into the MPLS network's IGP (OSPF or IS-IS). Either of the solutions can work, but this blog post shows the option of configuring iBGP next-hop-self. |
How to configure MPLS inter-AS option B?
In the following example topology two sites are connected with diferent Service Provider (SP) Layer-3 VPN MPLS networks. The sites belong to the same customer and need to communicate through the cooperation of the two SP networks. This is accomplished with inter-AS option B, which is configured on the ASBR PE routers R5 and R6.
The ASBR PE routers are connected with a single inter-AS interface using the command mpls bgp forwarding to enable label switching. This means, there is an end-to-end LSP between the PE router R2 and PE R8.
Also, the ASBR PE routers are not regular PEs in the sense that they do not have any VRF configured. Therefore, in order to receive BGP VPNv4 prefixes with the extended community Route Target (RT) value the command no bgp default route-target filter is needed under the BGP routing process.

Configuration:
R5 (ASBR PE)
R5#show run all | sec ^mpls ip__
mpls ip

R5#show run | sec ^mpls
mpls label range 500 599
mpls ldp router-id Loopback10 force

R5#show run int Lo10 | sec int
interface Loopback10
 ip address 5.5.5.5 255.255.255.255

R5#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R4 **
 ip address 10.3.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R5#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ASBR PE R6 **
 ip address 172.16.1.1 255.255.255.252
 duplex auto
 speed auto
 media-type rj45
 mpls bgp forwarding

R5#show run | sec ^router
router isis
 net 49.0010.0000.0000.0005.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 5.5.5.5
 bgp log-neighbor-changes
 no bgp default route-target filter
 neighbor 1.1.1.1 remote-as 65010
 neighbor 1.1.1.1 update-source Loopback10
 neighbor 172.16.1.2 remote-as 65020
 !
 address-family vpnv4
  neighbor 1.1.1.1 activate
  neighbor 1.1.1.1 send-community extended
  neighbor 1.1.1.1 next-hop-self
  neighbor 1.1.1.1 route-map RM-INTER-AS-RT out
  neighbor 172.16.1.2 activate
  neighbor 172.16.1.2 send-community extended
 exit-address-family

R5#show run | sec ^route-map
route-map RM-INTER-AS-RT permit 10
 match extcommunity CL-INTER-AS-RT
 set extcommunity rt 65010:2

R5#show run | sec ^ip ext
ip extcommunity-list standard CL-INTER-AS-RT permit rt 65020:1
R6 (ASBR PE)
R6#show run all | sec ^mpls ip__
mpls ip

R6#show run | sec ^mpls
mpls label range 600 699
mpls ldp router-id Loopback10 force

R6#show run int Lo10 | sec int
interface Loopback10
 ip address 6.6.6.6 255.255.255.255

R6#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to R7 **
 ip address 10.4.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls ip

R6#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ASBR PE R5 **
 ip address 172.16.1.2 255.255.255.252
 duplex auto
 speed auto
 media-type rj45
 mpls bgp forwarding

R6#show run | sec ^router
router ospf 10
 router-id 6.6.6.6
 network 6.6.6.6 0.0.0.0 area 0
 network 10.4.0.0 0.0.0.3 area 0
router bgp 65020
 bgp router-id 6.6.6.6
 bgp log-neighbor-changes
 no bgp default route-target filter
 neighbor 9.9.9.9 remote-as 65020
 neighbor 9.9.9.9 update-source Loopback10
 neighbor 172.16.1.1 remote-as 65010
 !
 address-family vpnv4
  neighbor 9.9.9.9 activate
  neighbor 9.9.9.9 send-community extended
  neighbor 9.9.9.9 next-hop-self
  neighbor 9.9.9.9 route-map RM-INTER-AS-RT out
  neighbor 172.16.1.1 activate
  neighbor 172.16.1.1 send-community extended
 exit-address-family

R6#show run | sec ^route-map
route-map RM-INTER-AS-RT permit 10
 match extcommunity CL-INTER-AS-RT
 set extcommunity rt 65020:2

R6#show run | sec ^ip ext
ip extcommunity-list standard CL-INTER-AS-RT permit rt 65010:1
R1 (RR)
R1#show run int Lo10 | sec int
interface Loopback10
 ip address 1.1.1.1 255.255.255.255

R1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R2 **
 ip address 10.1.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R1#show run | sec ^router
router isis
 net 49.0010.0000.0000.0001.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 1.1.1.1
 bgp log-neighbor-changes
 neighbor 2.2.2.2 remote-as 65010
 neighbor 2.2.2.2 update-source Loopback10
 neighbor 5.5.5.5 remote-as 65010
 neighbor 5.5.5.5 update-source Loopback10
 !
 address-family vpnv4
  neighbor 2.2.2.2 activate
  neighbor 2.2.2.2 send-community extended
  neighbor 2.2.2.2 route-reflector-client
  neighbor 5.5.5.5 activate
  neighbor 5.5.5.5 send-community extended
  neighbor 5.5.5.5 route-reflector-client
 exit-address-family
R9 (RR)
R9#show run int Lo10 | sec int
interface Loopback10
 ip address 9.9.9.9 255.255.255.255

R9#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R8 **
 ip address 10.6.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45

R9#show run | sec ^router
router ospf 10
 router-id 9.9.9.9
 network 9.9.9.9 0.0.0.0 area 0
 network 10.6.0.0 0.0.0.3 area 0
router bgp 65020
 bgp router-id 9.9.9.9
 bgp log-neighbor-changes
 neighbor 6.6.6.6 remote-as 65020
 neighbor 6.6.6.6 update-source Loopback10
 neighbor 8.8.8.8 remote-as 65020
 neighbor 8.8.8.8 update-source Loopback10
 !
 address-family vpnv4
  neighbor 6.6.6.6 activate
  neighbor 6.6.6.6 send-community extended
  neighbor 6.6.6.6 route-reflector-client
  neighbor 8.8.8.8 activate
  neighbor 8.8.8.8 send-community extended
  neighbor 8.8.8.8 route-reflector-client
 exit-address-family
R2 (PE)
R2#show run all | sec ^mpls ip__
mpls ip

R2#show run | sec ^mpls
mpls label range 200 299
mpls ldp router-id Loopback10 force

R2#show run | sec ^vrf
vrf definition Gold
 rd 65010:1
 !
 address-family ipv4
  route-target export 65010:1
  route-target import 65010:2
 exit-address-family

R2#show run int Lo10 | sec int
interface Loopback10
 ip address 2.2.2.2 255.255.255.255

R2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R3 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R2#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R3 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.1 255.255.255.252

R2#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to RR R1 **
 ip address 10.1.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 isis circuit-type level-2-only
 isis network point-to-point

R2#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to R4 **
 ip address 10.2.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R2#show run | sec ^router
router isis
 net 49.0010.0000.0000.0002.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 2.2.2.2
 bgp log-neighbor-changes
 neighbor 1.1.1.1 remote-as 65010
 neighbor 1.1.1.1 update-source Loopback10
 !
 address-family vpnv4
  neighbor 1.1.1.1 activate
  neighbor 1.1.1.1 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.1.0 mask 255.255.255.252
  neighbor 10.0.1.2 remote-as 65001
  neighbor 10.0.1.2 activate
 exit-address-family
R8 (PE)
R8#show run all | sec ^mpls ip__
mpls ip

R8#show run | sec ^mpls
mpls label range 800 899
mpls ldp router-id Loopback10 force

R8#show run | sec ^vrf
vrf definition Gold
 rd 65020:1
 !
 address-family ipv4
  route-target export 65020:1
  route-target import 65020:2
 exit-address-family

R8#show run int Lo10 | sec int
interface Loopback10
 ip address 8.8.8.8 255.255.255.255

R8#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R10 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R8#show run int Gi0/0.10 | sec int
interface GigabitEthernet0/0.10
 description ** to CE R10 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.1 255.255.255.252

R8#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to RR R9 **
 ip address 10.6.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45

R8#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to R7 **
 ip address 10.5.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls ip

R8#show run | sec ^router
router ospf 10
 router-id 8.8.8.8
 network 8.8.8.8 0.0.0.0 area 0
 network 10.5.0.0 0.0.0.3 area 0
 network 10.6.0.0 0.0.0.3 area 0
router bgp 65020
 bgp router-id 8.8.8.8
 bgp log-neighbor-changes
 neighbor 9.9.9.9 remote-as 65020
 neighbor 9.9.9.9 update-source Loopback10
 !
 address-family vpnv4
  neighbor 9.9.9.9 activate
  neighbor 9.9.9.9 send-community extended
 exit-address-family
 !
 address-family ipv4 vrf Gold
  network 10.0.2.0 mask 255.255.255.252
  neighbor 10.0.2.2 remote-as 65002
  neighbor 10.0.2.2 activate
 exit-address-family
R4
R4#show run all | sec ^mpls ip__
mpls ip

R4#show run | sec ^mpls
mpls label range 400 499
mpls ldp router-id Loopback10 force

R4#show run int Lo10 | sec int
interface Loopback10
 ip address 4.4.4.4 255.255.255.255

R4#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R2 **
 ip address 10.2.0.2 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ASBR PE R5 **
 ip address 10.3.0.1 255.255.255.252
 ip router isis
 duplex auto
 speed auto
 media-type rj45
 mpls ip
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run | sec ^router
router isis
 net 49.0010.0000.0000.0004.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R7
R7#show run all | sec ^mpls ip__
mpls ip

R7#show run | sec ^mpls
mpls label range 700 799
mpls ldp router-id Loopback10 force

R7#show run int Lo10 | sec int
interface Loopback10
 ip address 7.7.7.7 255.255.255.255

R7#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R8 **
 ip address 10.5.0.2 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls ip

R7#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to ASBR PE R6 **
 ip address 10.4.0.1 255.255.255.252
 ip ospf network point-to-point
 duplex auto
 speed auto
 media-type rj45
 mpls ip

R7#show run | sec ^router
router ospf 10
 router-id 7.7.7.7
 network 7.7.7.7 0.0.0.0 area 0
 network 10.4.0.0 0.0.0.3 area 0
 network 10.5.0.0 0.0.0.3 area 0
R3 (CE)
R3#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R3#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Host1 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R3#show run int Gi0/0.1 | sec int
interface GigabitEthernet0/0.1
 description ** to Host1 in VRF Gold (VLAN 1) **
 encapsulation dot1Q 1 native
 vrf forwarding Gold
 ip address 192.168.1.2 255.255.255.0

R3#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R3#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R2 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.1.2 255.255.255.252

R3#show run | sec ^router
router bgp 65001
 bgp router-id 3.3.3.3
 bgp log-neighbor-changes
 !
 address-family ipv4 vrf Gold
  network 192.168.1.0
  neighbor 10.0.1.1 remote-as 65010
  neighbor 10.0.1.1 activate
 exit-address-family
R10 (CE)
R10#show run | sec ^vrf
vrf definition Gold
 rd 1:1
 !
 address-family ipv4
 exit-address-family

R10#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Host2 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R10#show run int Gi0/0.1 | sec int
interface GigabitEthernet0/0.1
 description ** to Host2 in VRF Gold (VLAN 1) **
 encapsulation dot1Q 1 native
 vrf forwarding Gold
 ip address 192.168.2.2 255.255.255.0

R10#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to PE R8 **
 no ip address
 duplex auto
 speed auto
 media-type rj45

R10#show run int Gi0/1.10 | sec int
interface GigabitEthernet0/1.10
 description ** to PE R8 in VRF Gold **
 encapsulation dot1Q 10
 vrf forwarding Gold
 ip address 10.0.2.2 255.255.255.252

R10#show run | sec ^router
router bgp 65002
 bgp router-id 10.10.10.10
 bgp log-neighbor-changes
 !
 address-family ipv4 vrf Gold
  network 192.168.2.0
  neighbor 10.0.2.1 remote-as 65020
  neighbor 10.0.2.1 activate
 exit-address-family
Host1
Host1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R3 **
 ip address 192.168.1.1 255.255.255.0
 duplex auto
 speed auto
 media-type rj45

Host1#show run | sec ^ip route
ip route 0.0.0.0 0.0.0.0 192.168.1.2
Host2
Host2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE R10 **
 ip address 192.168.2.1 255.255.255.0
 duplex auto
 speed auto
 media-type rj45

Host2#show run | sec ^ip route
ip route 0.0.0.0 0.0.0.0 192.168.2.2
Host1#trace 192.168.2.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.2.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.2 2 msec
  2 10.0.1.1 2 msec
  3 10.2.0.2 [MPLS: Labels 402/507 Exp 0] 7 msec
  4 10.3.0.2 [MPLS: Label 507 Exp 0] 6 msec
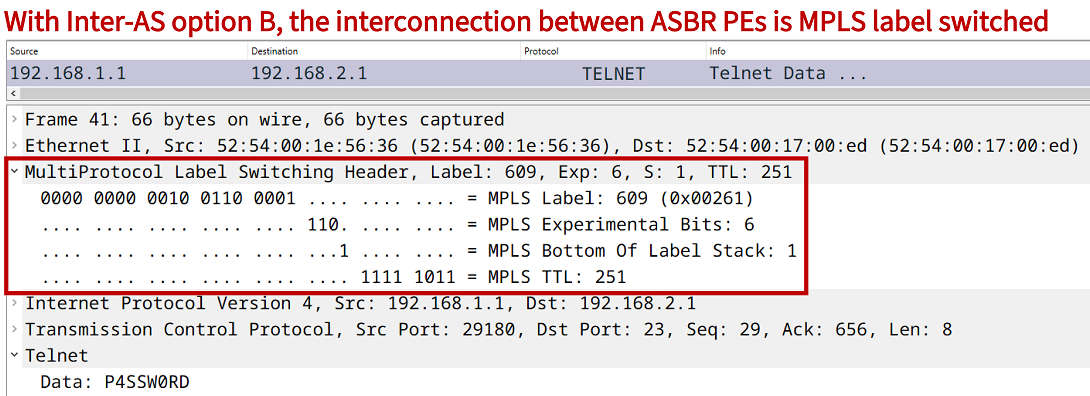
  5 172.16.1.2 [MPLS: Label 609 Exp 0] 7 msec            « Inter-AS interconnection is label switched
  6 10.4.0.1 [MPLS: Labels 701/805 Exp 0] 7 msec
  7 10.0.2.1 [MPLS: Label 805 Exp 0] 6 msec
  8 10.0.2.2 6 msec
  9 192.168.2.1 8 msec


Host1#ping 192.168.2.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 192.168.2.1, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 69/70/72 ms


Host2#trace 192.168.1.1 probe 1
Type escape sequence to abort.
Tracing the route to 192.168.1.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.2.2 1 msec
  2 10.0.2.1 24 msec
  3 10.5.0.2 [MPLS: Labels 702/609 Exp 0] 69 msec
  4 10.4.0.2 [MPLS: Label 609 Exp 0] 71 msec
  5 172.16.1.1 [MPLS: Label 507 Exp 0] 70 msec
  6 10.3.0.1 [MPLS: Labels 403/206 Exp 0] 72 msec
  7 10.0.1.1 [MPLS: Label 206 Exp 0] 50 msec
  8 10.0.1.2 70 msec
  9 192.168.1.1 69 msec


Host2#ping 192.168.1.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 192.168.1.1, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 68/71/77 ms
The label range is configured on each Label Switch Router (LSR) to identify them more easily, this means that R5 uses the range 500 - 599, R6 uses 600 - 699 and so on. It is visible in the above outputs that the inter-AS interconnection is label switched.
An important aspect of the inter-AS option B solution is that the Route Target values are inherited from the neighboring Service Provider's PE router. In other words, RR R1 receives the RT value assigned by PE R8. Due to this behavior, the ASBR PE routers rewrite the RT values to match those used within their own local MPLS network.
Thus, ASBR PE R5 receives the RT value 65020:1 from R6. This value is rewritten on ASBR PE R5 to 65010:2, and advertised to the RR R1. The same happens vice versa on ASBR PE R6 which rewrites the received RT value and uses 65020:2 as the new value.
R5#show ip bgp vpnv4 all 192.168.2.0
BGP routing table entry for 65020:1:192.168.2.0/24, version 5        « ASBR PE R5 receives Site 2 VPNv4 prefix from other SP (from ASBR PE R6)
Paths: (1 available, best #1, no table)
  Advertised to update-groups:
     2
  Refresh Epoch 1
  65020 65002
    172.16.1.2 (via default) from 172.16.1.2 (6.6.6.6)
      Origin IGP, localpref 100, valid, external, best
      Extended Community: RT:65020:1                                 « ASBR PE R5 receives RT 65020:1
      mpls labels in/out 509/611
      rx pathid: 0, tx pathid: 0x0


R1#show ip bgp vpnv4 all 192.168.2.0
BGP routing table entry for 65020:1:192.168.2.0/24, version 5
Paths: (1 available, best #1, no table)
Flag: 0x100
  Advertised to update-groups:
     1
  Refresh Epoch 1
  65020 65002, (Received from a RR-client)
    5.5.5.5 (metric 30) (via default) from 5.5.5.5 (5.5.5.5)
      Origin IGP, metric 0, localpref 100, valid, internal, best
      Extended Community: RT:65010:2                                 « RR R1 receives rewritten value 65010:2 (value rewritten by ASBR PE R5)
      mpls labels in/out nolabel/509
      rx pathid: 0, tx pathid: 0x0


R2#show ip bgp vpnv4 vrf Gold 192.168.2.0
BGP routing table entry for 65010:1:192.168.2.0/24, version 7
Paths: (1 available, best #1, table Gold)
Flag: 0x100
  Advertised to update-groups:
     1
  Refresh Epoch 1
  65020 65002, imported path from 65020:1:192.168.2.0/24 (global)    « Notice the Route Distinguisher 65020:1 does not change
    5.5.5.5 (metric 20) (via default) from 1.1.1.1 (1.1.1.1)
      Origin IGP, metric 0, localpref 100, valid, internal, best
      Extended Community: RT:65010:2                                 « PE Router R2 imports Site 2 route with RT 65010:2
      Originator: 5.5.5.5, Cluster list: 1.1.1.1
      mpls labels in/out nolabel/509
      rx pathid: 0, tx pathid: 0x0