EVPN MPLS Multihoming Dual PE with All-Active Redundancy
Table of Contents
Jump to section:
What is EVPN multihoming?
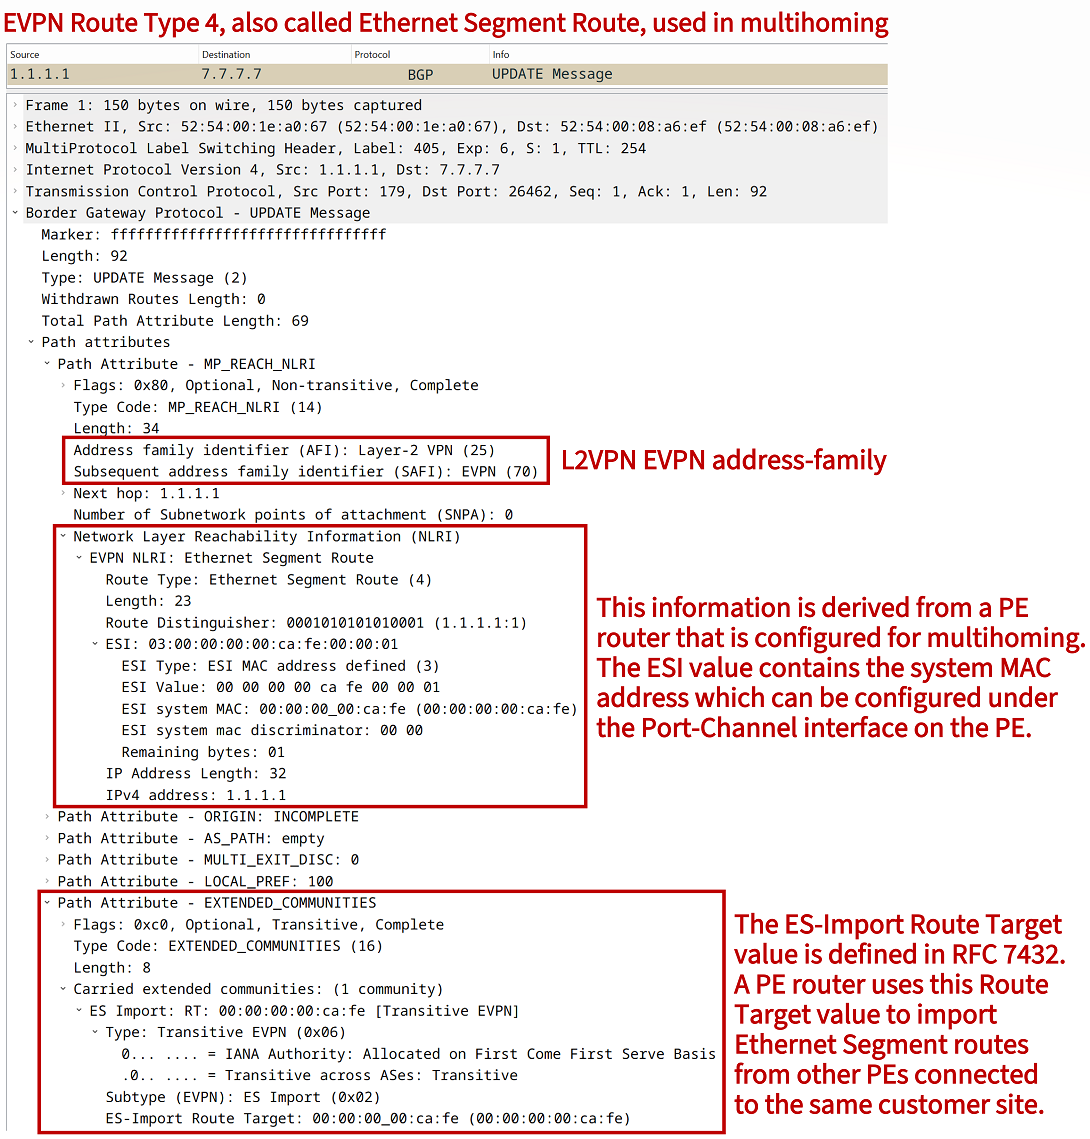
The EVPN control plane allows for dual edge devices and multihoming designs. This includes two variants, multihoming for EVPN with VXLAN and for EVPN with MPLS. EVPN MPLS multihoming enables deploying two Provider Edge (PE) routers connected to a single Customer Edge (CE) device. Such a design improves resiliency to network failures. EVPN Route Type 1 and 4 specifically enable multihomed deployments.
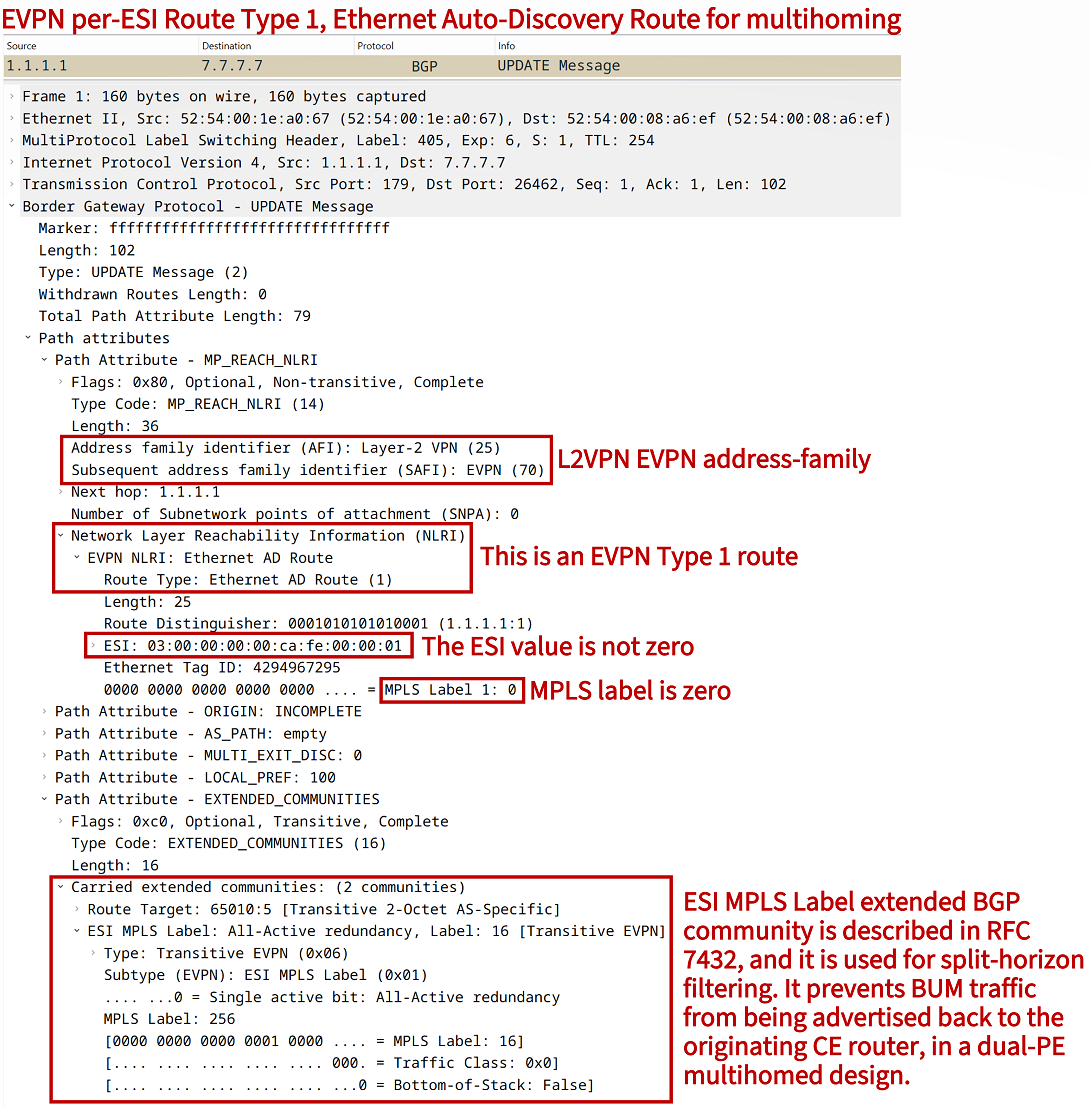
EVPN multihoming uses the per-ESI Route Type 1 Ethernet Auto-Discovery Route. This is similar to the per-EVI Route Type 1, however there are multiple differences. For example, the per-ESI Route Type 1 has a non-zero ESI value and it carries the MPLS label value 0, as shown in the following capture.
How to configure EVPN multihoming?
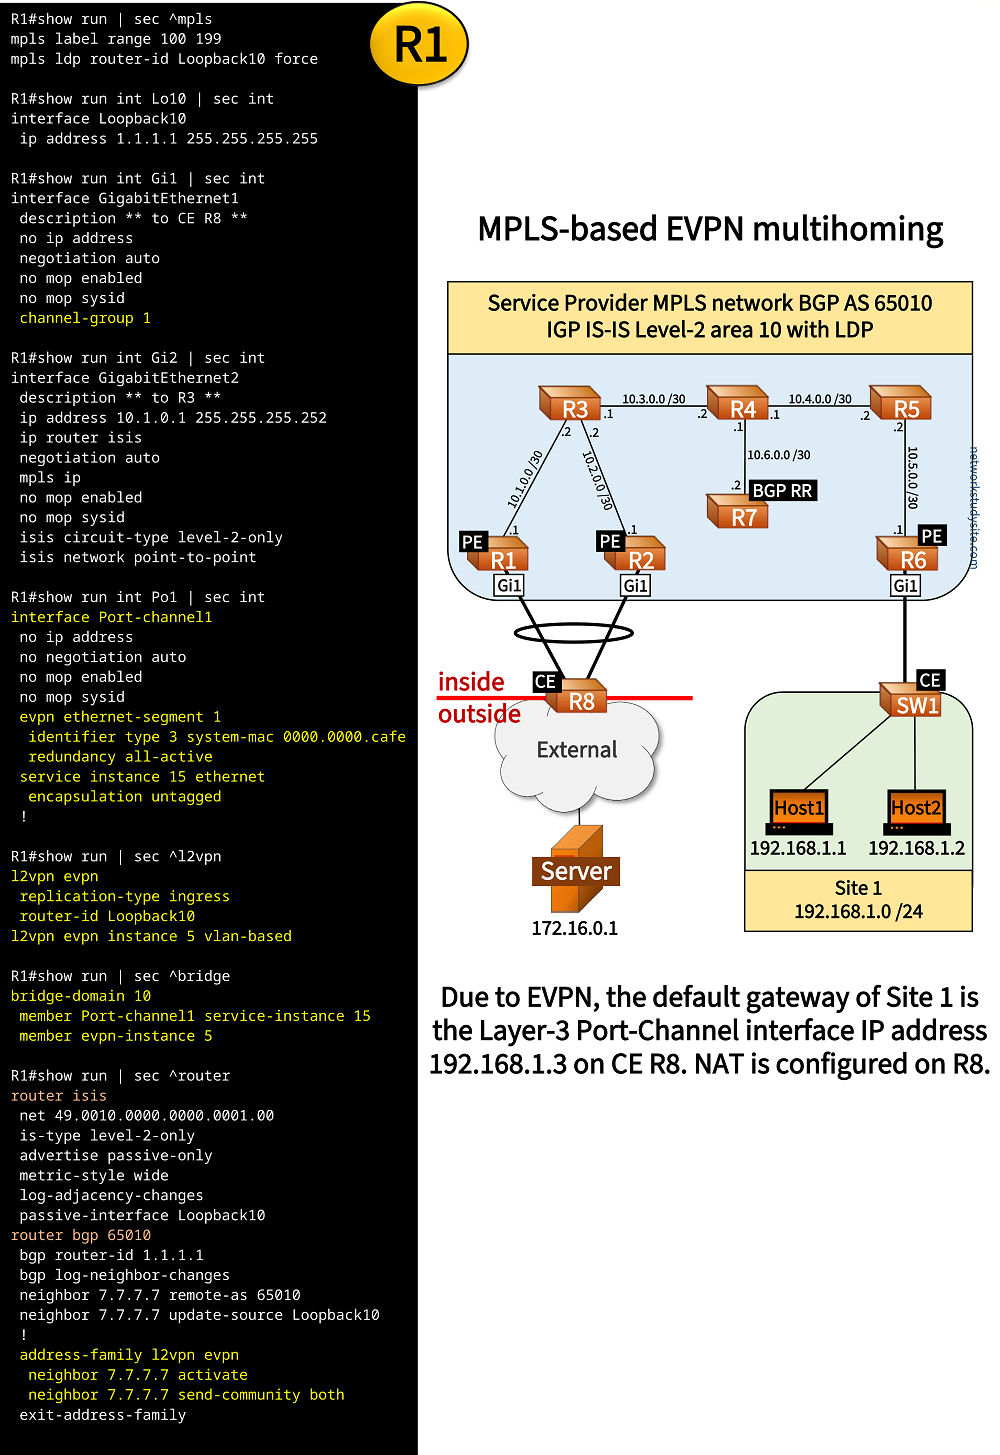
In the following example scenario, Site 1 is connected through EVPN to the CE router R8. The PE-facing interface IP address on R8 is reachable for the hosts in Site 1 within the same subnet 192.168.1.0 /24. CE R8 is connected with PE routers R1 and R2 which have EVPN all-active multihoming deployed. The two links connecting R8 to the EVPN network are bundled into a single Layer-3 Port-Channel interface. Thus, the default gateway IP address for the hosts in Site 1 is the Port-Channel interface IP address 192.168.1.3 which is configured on CE R8.
Network Address Translation (NAT) is also configured on CE R8, and provides access for the hosts to an external network where the Server (172.16.0.1) resides. The NAT inside interface is the PE-facing Port-Channel interface on R8. Each host uses the single outside interface IP address on CE R8 (NAT overload).
As a result, the hosts can use a default gateway IP address in their local subnet through EVPN to reach the Server. Note this is a hypothetical scenario designed only to practice and demonstrate how the technologies can work together.
Configuration:
R1 (PE)
R1#show run all | sec ^mpls ip__
mpls ip

R1#show run | sec ^mpls
mpls label range 100 199
mpls ldp router-id Loopback10 force

R1#show run int Lo10 | sec int
interface Loopback10
 ip address 1.1.1.1 255.255.255.255

R1#show run int Gi1 | sec int
interface GigabitEthernet1
 description ** to CE R8 **
 no ip address
 negotiation auto
 no mop enabled
 no mop sysid
 channel-group 1

R1#show run int Gi2 | sec int
interface GigabitEthernet2
 description ** to R3 **
 ip address 10.1.0.1 255.255.255.252
 ip router isis
 negotiation auto
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only
 isis network point-to-point

R1#show run int Po1 | sec int
interface Port-channel1
 no ip address
 no negotiation auto
 no mop enabled
 no mop sysid
 evpn ethernet-segment 1
  identifier type 3 system-mac 0000.0000.cafe
  redundancy all-active
 service instance 15 ethernet
  encapsulation untagged
 !

R1#show run | sec ^l2vpn
l2vpn evpn
 replication-type ingress
 router-id Loopback10
l2vpn evpn instance 5 vlan-based

R1#show run | sec ^bridge
bridge-domain 10
 member Port-channel1 service-instance 15
 member evpn-instance 5

R1#show run | sec ^router
router isis
 net 49.0010.0000.0000.0001.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 1.1.1.1
 bgp log-neighbor-changes
 neighbor 7.7.7.7 remote-as 65010
 neighbor 7.7.7.7 update-source Loopback10
 !
 address-family l2vpn evpn
  neighbor 7.7.7.7 activate
  neighbor 7.7.7.7 send-community both
 exit-address-family
R2 (PE)
R2#show run all | sec ^mpls ip__
mpls ip

R2#show run | sec ^mpls
mpls label range 200 299
mpls ldp router-id Loopback10 force

R2#show run int Lo10 | sec int
interface Loopback10
 ip address 2.2.2.2 255.255.255.255

R2#show run int Gi1 | sec int
interface GigabitEthernet1
 description ** to CE R8 **
 no ip address
 negotiation auto
 no mop enabled
 no mop sysid
 channel-group 1

R2#show run int Gi2 | sec int
interface GigabitEthernet2
 description ** to R3 **
 ip address 10.2.0.1 255.255.255.252
 ip router isis
 negotiation auto
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only
 isis network point-to-point

R2#show run int Po1 | sec int
interface Port-channel1
 no ip address
 no negotiation auto
 no mop enabled
 no mop sysid
 evpn ethernet-segment 1
  identifier type 3 system-mac 0000.0000.cafe
  redundancy all-active
 service instance 15 ethernet
  encapsulation untagged
 !

R2#show run | sec ^l2vpn
l2vpn evpn
 replication-type ingress
 router-id Loopback10
l2vpn evpn instance 5 vlan-based

R2#show run | sec ^bridge
bridge-domain 10
 member Port-channel1 service-instance 15
 member evpn-instance 5

R2#show run | sec ^router
router isis
 net 49.0010.0000.0000.0002.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 2.2.2.2
 bgp log-neighbor-changes
 neighbor 7.7.7.7 remote-as 65010
 neighbor 7.7.7.7 update-source Loopback10
 !
 address-family l2vpn evpn
  neighbor 7.7.7.7 activate
  neighbor 7.7.7.7 send-community both
 exit-address-family
R6 (PE)
R6#show run all | sec ^mpls ip__
mpls ip

R6#show run | sec ^mpls
mpls label range 600 699
mpls ldp router-id Loopback10 force

R6#show run int Lo10 | sec int
interface Loopback10
 ip address 6.6.6.6 255.255.255.255

R6#show run int Gi1 | sec int
interface GigabitEthernet1
 description ** to CE SW1 **
 no ip address
 negotiation auto
 no mop enabled
 no mop sysid
 service instance 30 ethernet
  encapsulation untagged
 !

R6#show run int Gi2 | sec int
interface GigabitEthernet2
 description ** to R5 **
 ip address 10.5.0.1 255.255.255.252
 ip router isis
 negotiation auto
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only
 isis network point-to-point

R6#show run | sec ^l2vpn
l2vpn evpn
 replication-type ingress
 router-id Loopback10
l2vpn evpn instance 5 vlan-based

R6#show run | sec ^bridge
bridge-domain 10
 member GigabitEthernet1 service-instance 30
 member evpn-instance 5

R6#show run | sec ^router
router isis
 net 49.0010.0000.0000.0006.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 6.6.6.6
 bgp log-neighbor-changes
 neighbor 7.7.7.7 remote-as 65010
 neighbor 7.7.7.7 update-source Loopback10
 !
 address-family l2vpn evpn
  neighbor 7.7.7.7 activate
  neighbor 7.7.7.7 send-community both
 exit-address-family
R8 (CE)
R8#show run int Gi1 | sec int
interface GigabitEthernet1
 description ** to PE R1 **
 no ip address
 negotiation auto
 no mop enabled
 no mop sysid
 channel-group 10

R8#show run int Gi2 | sec int
interface GigabitEthernet2
 description ** to PE R2 **
 no ip address
 negotiation auto
 no mop enabled
 no mop sysid
 channel-group 10

R8#show run int Po10 | sec int
interface Port-channel10
 description ** Layer-3 Port-Channel EVPN multihoming **
 ip address 192.168.1.3 255.255.255.0
 ip nat inside
 no negotiation auto
 no mop enabled
 no mop sysid

R8#show run int Gi3 | sec int
interface GigabitEthernet3
 description ** to Server **
 ip address 172.16.0.2 255.255.255.252
 ip nat outside
 negotiation auto
 no mop enabled
 no mop sysid

R8#show run | sec ^ip nat
ip nat inside source list ACL-NAT interface GigabitEthernet3 overload

R8#show run | sec ^ip access
ip access-list standard ACL-NAT
 10 permit 192.168.1.0 0.0.0.255
SW1 (CE)
SW1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to PE R6 **
 switchport trunk encapsulation dot1q
 switchport mode trunk
 negotiation auto

SW1#show run int Gi0/1 | sec int
interface GigabitEthernet0/1
 description ** to Host1 **
 switchport mode access
 negotiation auto

SW1#show run int Gi0/2 | sec int
interface GigabitEthernet0/2
 description ** to Host2 **
 switchport mode access
 negotiation auto
R3
R3#show run all | sec ^mpls ip__
mpls ip

R3#show run | sec ^mpls
mpls label range 300 399
mpls ldp router-id Loopback10 force

R3#show run int Lo10 | sec int
interface Loopback10
 ip address 3.3.3.3 255.255.255.255

R3#show run int Gi1 | sec int
interface GigabitEthernet1
 description ** to PE R1 **
 ip address 10.1.0.2 255.255.255.252
 ip router isis
 negotiation auto
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only
 isis network point-to-point

R3#show run int Gi2 | sec int
interface GigabitEthernet2
 description ** to PE R2 **
 ip address 10.2.0.2 255.255.255.252
 ip router isis
 negotiation auto
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only
 isis network point-to-point

R3#show run int Gi3 | sec int
interface GigabitEthernet3
 description ** to R4 **
 ip address 10.3.0.1 255.255.255.252
 ip router isis
 negotiation auto
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only
 isis network point-to-point

R3#show run | sec ^router
router isis
 net 49.0010.0000.0000.0003.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R4
R4#show run all | sec ^mpls ip__
mpls ip

R4#show run | sec ^mpls
mpls label range 400 499
mpls ldp router-id Loopback10 force

R4#show run int Lo10 | sec int
interface Loopback10
 ip address 4.4.4.4 255.255.255.255

R4#show run int Gi1 | sec int
interface GigabitEthernet1
 description ** to R3 **
 ip address 10.3.0.2 255.255.255.252
 ip router isis
 negotiation auto
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run int Gi2 | sec int
interface GigabitEthernet2
 description ** to R5 **
 ip address 10.4.0.1 255.255.255.252
 ip router isis
 negotiation auto
 mpls ip
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only
 isis network point-to-point

R4#show run int Gi3 | sec int
interface GigabitEthernet3
 description ** to BGP RR R7 **
 ip address 10.6.0.1 255.255.255.252
 ip router isis
 negotiation auto
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only

R4#show run | sec ^router
router isis
 net 49.0010.0000.0000.0004.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
R7 (BGP RR)
R7#show run int Lo10 | sec int
interface Loopback10
 ip address 7.7.7.7 255.255.255.255

R7#show run int Gi1 | sec int
interface GigabitEthernet1
 description ** to R4 **
 ip address 10.6.0.2 255.255.255.252
 ip router isis
 negotiation auto
 no mop enabled
 no mop sysid
 isis circuit-type level-2-only

R7#show run | sec ^router
router isis
 net 49.0010.0000.0000.0007.00
 is-type level-2-only
 advertise passive-only
 metric-style wide
 log-adjacency-changes
 passive-interface Loopback10
router bgp 65010
 bgp router-id 7.7.7.7
 bgp log-neighbor-changes
 neighbor 1.1.1.1 remote-as 65010
 neighbor 1.1.1.1 update-source Loopback10
 neighbor 2.2.2.2 remote-as 65010
 neighbor 2.2.2.2 update-source Loopback10
 neighbor 6.6.6.6 remote-as 65010
 neighbor 6.6.6.6 update-source Loopback10
 !
 address-family l2vpn evpn
  neighbor 1.1.1.1 activate
  neighbor 1.1.1.1 send-community both
  neighbor 1.1.1.1 route-reflector-client
  neighbor 2.2.2.2 activate
  neighbor 2.2.2.2 send-community both
  neighbor 2.2.2.2 route-reflector-client
  neighbor 6.6.6.6 activate
  neighbor 6.6.6.6 send-community both
  neighbor 6.6.6.6 route-reflector-client
 exit-address-family
Host1
Host1#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE SW1 **
 ip address 192.168.1.1 255.255.255.0
 duplex auto
 speed auto
 media-type rj45

Host1#show run | sec ^ip route
ip route 0.0.0.0 0.0.0.0 192.168.1.3
Host2
Host2#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to CE SW1 **
 ip address 192.168.1.2 255.255.255.0
 duplex auto
 speed auto
 media-type rj45

Host2#show run | sec ^ip route
ip route 0.0.0.0 0.0.0.0 192.168.1.3
Server
Server#show run int Gi0/0 | sec int
interface GigabitEthernet0/0
 description ** to Internet (CE R8) **
 ip address 172.16.0.1 255.255.255.252
 duplex auto
 speed auto
 media-type rj45
Host1#ping 172.16.0.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 172.16.0.1, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 49/49/50 ms               « Host1 can reach the Server


Host1#trace 172.16.0.1 pr 1
Type escape sequence to abort.
Tracing the route to 172.16.0.1
VRF info: (vrf in name/id, vrf out name/id)
  1 192.168.1.3 27 msec                            « CE R8 Port-Channel interface IP address
  2 172.16.0.1 12 msec                             « Due to EVPN-MPLS it looks like the Server is only two hops away


Host2#ping 172.16.0.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 172.16.0.1, timeout is 2 seconds:
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 48/49/50 ms               « Host2 can reach the Server


Host1#show arp
Protocol  Address          Age (min)  Hardware Addr   Type   Interface
Internet  192.168.1.1             -   5254.0018.a67b  ARPA   GigabitEthernet0/0
Internet  192.168.1.3             0   001e.bd2e.dac9  ARPA   GigabitEthernet0/0       « CE R8 Port-Channel interface MAC address in ARP cache


R8#show int Port-Channel10 | sec bia
  Hardware is GEChannel, address is 001e.bd2e.dac9 (bia 001e.bd2e.dac9)


R8#show ip nat translations                         « NAT translations on CE R8
Pro  Inside global         Inside local          Outside local         Outside global
icmp 172.16.0.2:5          192.168.1.2:5         172.16.0.1:5          172.16.0.1:5
icmp 172.16.0.2:8          192.168.1.1:8         172.16.0.1:8          172.16.0.1:8
Total number of translations: 2
EVPN Route Type 4 is an Ethernet Segment Route and supports the election of a Designated Forwarder (DF) between PE R1 and PE R2. The DF is a PE router that will send Broadcast, Unknown Unicast, and Multicast (BUM) traffic connected to the CE router R8. Only one DF is elected per Ethernet Segment. The following output from the BGP RR provides insights into these route types.
R7#show ip bgp l2vpn evpn all sum | beg Ne
Neighbor        V           AS MsgRcvd MsgSent   TblVer  InQ OutQ Up/Down  State/PfxRcd
1.1.1.1         4        65010     159     232       75    0    0 02:10:53        4        « 4 EVPN routes received from multihoming PE router
2.2.2.2         4        65010     164     240       75    0    0 02:10:51        5
6.6.6.6         4        65010     176     194       75    0    0 02:10:51        3


R7#show ip bgp l2vpn evpn route-type 4 | include BGP routing table                               « These are Type 4 routes received on the RR
BGP routing table entry for [4][1.1.1.1:1][0300000000CAFE000001][32][1.1.1.1]/23, version 18
BGP routing table entry for [4][2.2.2.2:1][0300000000CAFE000001][32][2.2.2.2]/23, version 20


R7#show ip bgp l2vpn evpn route-type 1 | include BGP routing table                               « These are Type 1 routes
BGP routing table entry for [1][1.1.1.1:3][0300000000CAFE000001][4294967295]/23, version 17      « This is sent by PE R1
BGP routing table entry for [1][1.1.1.1:5][0300000000CAFE000001][0]/23, version 15
BGP routing table entry for [1][2.2.2.2:3][0300000000CAFE000001][4294967295]/23, version 19
BGP routing table entry for [1][2.2.2.2:5][0300000000CAFE000001][0]/23, version 11
MAC addresses are carried with BGP updates using Route Type 2 MAC/IP advertisement routes. This includes the MAC address of the Port-Channel interface on CE R8, and the MAC address of Host1 and Host2 in Site 1. The following output lists these routes received on the RR.
R7#show ip bgp l2vpn evpn route-type 2 | include BGP routing table
BGP routing table entry for [2][2.2.2.2:5][0][48][001EBD2EDAC9][0][*]/20, version 30         « MAC address of Port-Channel interface on CE R8
BGP routing table entry for [2][6.6.6.6:5][0][48][5254000D020E][0][*]/20, version 4          « MAC address of Host2
BGP routing table entry for [2][6.6.6.6:5][0][48][52540013D2CD][0][*]/20, version 5
BGP routing table entry for [2][6.6.6.6:5][0][48][52540018A67B][0][*]/20, version 6          « MAC address of Host1


R7#show ip bgp l2vpn evpn route-type 2 0 001EBD2EDAC9 *
BGP routing table entry for [2][2.2.2.2:5][0][48][001EBD2EDAC9][0][*]/20, version 30         « EVPN Route Type 2 with CE R8 Port-Channel MAC
Paths: (1 available, best #1, table EVPN-BGP-Table)
  Flag: 0x100
  Advertised to update-groups:
     1
  Refresh Epoch 1
  Local, (Received from a RR-client)
    2.2.2.2 (metric 30) (via default) from 2.2.2.2 (2.2.2.2)                                 « This update is sent by PE R2
      Origin incomplete, metric 0, localpref 100, valid, internal, best
      EVPN ESI: 0300000000CAFE000001, Label1 201                                             « PE R2 assigns the VPN service label 209 to this route
      Extended Community: RT:65010:5
      rx pathid: 0, tx pathid: 0x0
      net: 0x7F0C9AB7E060, path: 0x7F0C6A088760, pathext: 0x7F0C9AB93EB8
      flags: net: 0x100, path: 0x3, pathext: 0xA1
      attribute: 0x7F0C9AB6F0A0, ref: 6
      Updated on May 28 2025 08:08:21 UTC
EVPN Route Type (RT) 1 and 4 play an important role in multihomed designs as described in the above sections. The following EVPN RT 1 and RT 4 updates provide further details from the perspective of the Route Reflector.
R7#show ip bgp l2vpn evpn route-type 1
BGP routing table entry for [1][1.1.1.1:1][0300000000CAFE000001][4294967295]/23, version 22       « ESI value used in both RT 1 and RT 4
Paths: (1 available, best #1, table EVPN-BGP-Table)
  Advertised to update-groups:
     1
  Refresh Epoch 1
  Local, (Received from a RR-client)
    1.1.1.1 (metric 30) (via default) from 1.1.1.1 (1.1.1.1)                 « Received from PE R1
      Origin incomplete, metric 0, localpref 100, valid, internal, best
      Rcvd Label: 0, Local Label: None
      Extended Community: RT:65010:5 EVPN LABEL:0x0:Label-256                « ESI MPLS Label used in per-ESI EVPN Route Type 1
      rx pathid: 0, tx pathid: 0x0
      net: 0x7F0C9AB7E990, path: 0x7F0C6A088CD0, pathext: 0x7F0C9AB94338
      flags: net: 0x0, path: 0x3, pathext: 0x81
      attribute: 0x7F0C9AB6F310, ref: 3
      Updated on May 28 2025 08:07:55 UTC
BGP routing table entry for [1][1.1.1.1:5][0300000000CAFE000001][0]/23, version 26
Paths: (1 available, best #1, table EVPN-BGP-Table)
  Advertised to update-groups:
     1
  Refresh Epoch 1
  Local, (Received from a RR-client)
    1.1.1.1 (metric 30) (via default) from 1.1.1.1 (1.1.1.1)
      Origin incomplete, metric 0, localpref 100, valid, internal, best
      Rcvd Label: 101, Local Label: None
      Extended Community: RT:65010:5
      rx pathid: 0, tx pathid: 0x0
      net: 0x7F0C9AB7E370, path: 0x7F0C6A088B00, pathext: 0x7F0C9AB94098
      flags: net: 0x0, path: 0x3, pathext: 0x81
      attribute: 0x7F0C9AB6F0A0, ref: 4
      Updated on May 28 2025 08:07:58 UTC
BGP routing table entry for [1][2.2.2.2:1][0300000000CAFE000001][4294967295]/23, version 24
Paths: (1 available, best #1, table EVPN-BGP-Table)
  Flag: 0x100
  Advertised to update-groups:
     1
  Refresh Epoch 1
  Local, (Received from a RR-client)
    2.2.2.2 (metric 30) (via default) from 2.2.2.2 (2.2.2.2)                 « Received from PE R2
      Origin incomplete, metric 0, localpref 100, valid, internal, best
      Rcvd Label: 0, Local Label: None
      Extended Community: RT:65010:5 EVPN LABEL:0x0:Label-256                « ESI MPLS Label used in per-ESI EVPN Route Type 1
      rx pathid: 0, tx pathid: 0x0
      net: 0x7F0C9AB7F2C0, path: 0x7F0C6A089240, pathext: 0x7F0C9AB93FD8
      flags: net: 0x100, path: 0x3, pathext: 0xA1
      attribute: 0x7F0C9AB6F310, ref: 3
      Updated on May 28 2025 08:07:56 UTC
BGP routing table entry for [1][2.2.2.2:5][0300000000CAFE000001][0]/23, version 28
Paths: (1 available, best #1, table EVPN-BGP-Table)
  Flag: 0x100
  Advertised to update-groups:
     1
  Refresh Epoch 1
  Local, (Received from a RR-client)
    2.2.2.2 (metric 30) (via default) from 2.2.2.2 (2.2.2.2)
      Origin incomplete, metric 0, localpref 100, valid, internal, best
      Rcvd Label: 201, Local Label: None
      Extended Community: RT:65010:5
      rx pathid: 0, tx pathid: 0x0
      net: 0x7F0C9AB7E680, path: 0x7F0C6A088930, pathext: 0x7F0C9AB93F78
      flags: net: 0x100, path: 0x3, pathext: 0xA1
      attribute: 0x7F0C9AB6F0A0, ref: 4
      Updated on May 28 2025 08:07:58 UTC


--------------------------------------------------------------------------------------------------------


R7#show ip bgp l2vpn evpn route-type 4
BGP routing table entry for [4][1.1.1.1:1][0300000000CAFE000001][32][1.1.1.1]/23, version 23
Paths: (1 available, best #1, table EVPN-BGP-Table)
  Advertised to update-groups:
     1
  Refresh Epoch 1
  Local, (Received from a RR-client)
    1.1.1.1 (metric 30) (via default) from 1.1.1.1 (1.1.1.1)               « Received from PE R1
      Origin incomplete, metric 0, localpref 100, valid, internal, best
      Extended Community: EVPN ES-IMPORT:0x0:0x0:0xCAFE                    « ES-Import community
      rx pathid: 0, tx pathid: 0x0
      net: 0x7F0C9AB7E808, path: 0x7F0C6A088BE8, pathext: 0x7F0C9AB942D8
      flags: net: 0x0, path: 0x3, pathext: 0x81
      attribute: 0x7F0C9AB6F1D8, ref: 3
      Updated on May 28 2025 08:07:55 UTC
BGP routing table entry for [4][2.2.2.2:1][0300000000CAFE000001][32][2.2.2.2]/23, version 25
Paths: (1 available, best #1, table EVPN-BGP-Table)
  Flag: 0x100
  Advertised to update-groups:
     1
  Refresh Epoch 1
  Local, (Received from a RR-client)
    2.2.2.2 (metric 30) (via default) from 2.2.2.2 (2.2.2.2)               « Received from PE R2
      Origin incomplete, metric 0, localpref 100, valid, internal, best
      Extended Community: EVPN ES-IMPORT:0x0:0x0:0xCAFE                    « ES-Import community
      rx pathid: 0, tx pathid: 0x0
      net: 0x7F0C9AB7F138, path: 0x7F0C6A089158, pathext: 0x7F0C9AB94038
      flags: net: 0x100, path: 0x3, pathext: 0xA1
      attribute: 0x7F0C9AB6F1D8, ref: 3
      Updated on May 28 2025 08:07:56 UTC
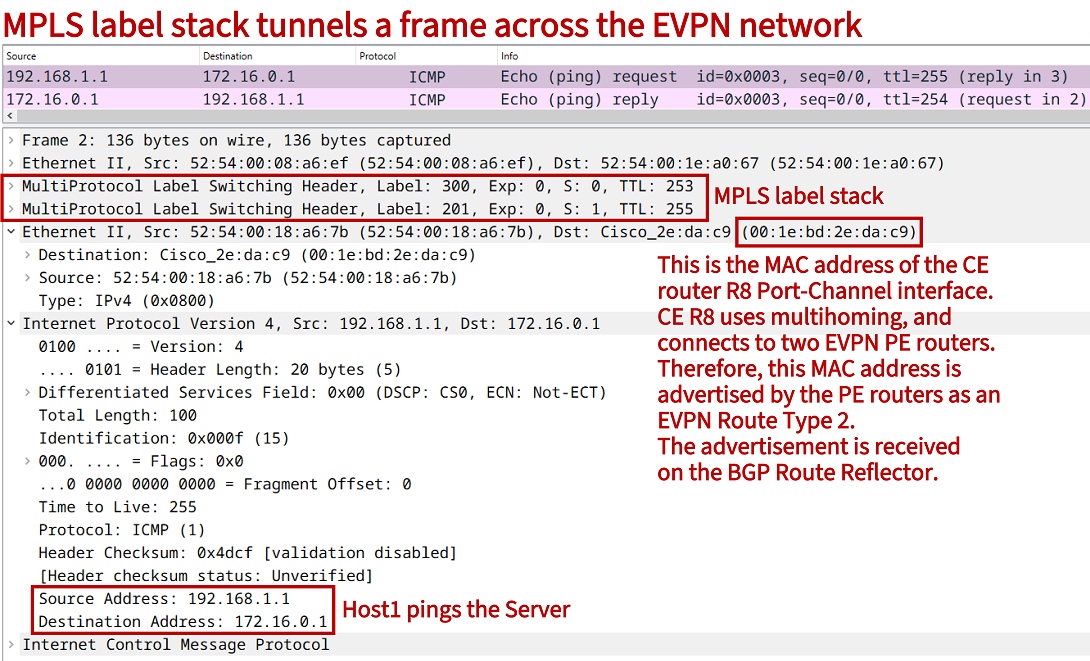
The following packet capture shows traffic sent from Host1 to the Server. The capture is taken within the EVPN network and displays the MPLS label stack attached, including the VPN Service Label 209 which is assigned by the PE R2.
R7#show ip bgp l2vpn evpn route-type 2 0 001EBD2EDAC9 *
BGP routing table entry for [2][2.2.2.2:5][0][48][001EBD2EDAC9][0][*]/20, version 42      « MAC address in above capture shown on the BGP RR
Paths: (1 available, best #1, table EVPN-BGP-Table)
  Advertised to update-groups:
     1
  Refresh Epoch 1
  Local, (Received from a RR-client)
    2.2.2.2 (metric 30) (via default) from 2.2.2.2 (2.2.2.2)
      Origin incomplete, metric 0, localpref 100, valid, internal, best
      EVPN ESI: 0300000000CAFE000001, Label1 201                                    « VPN service label 201 is also visible in the above packet capture
      Extended Community: RT:65010:5
      rx pathid: 0, tx pathid: 0x0
      net: 0x7F0C9AB7E060, path: 0x7F0C6A088EA0, pathext: 0x7F0C9AB941B8
      flags: net: 0x0, path: 0x3, pathext: 0x81
      attribute: 0x7F0C9AB6F0A0, ref: 6
      Updated on May 28 2025 08:32:13 UTC
The following show commands verify the operation of the EVPN multihoming network. The outputs are taken from the PE router R2 and confirm the status of the Ethernet Virtual Instance (EVI), the Ethernet Segment (ES) and the Bridge-Domain (BD).
R1#show l2vpn evpn summary
L2VPN EVPN
  EVPN Instances (excluding point-to-point): 1
    VLAN Aware:   0
    VLAN Based:   1
    VLAN Bundle:  0
  Bridge Domains: 1
  BGP: ASN 65010, address-family l2vpn evpn configured
  Router ID: 1.1.1.1
  Label Allocation Mode: Per-BD
  Global Replication Type: Ingress
  Connectivity to Core: UP
  MAC Duplication: seconds 180 limit 5
  MAC Addresses: 0
    Local:     0
    Remote:    0
    Duplicate: 0
  Maximum number of Route Targets per EAD-ES route: 200
  Multi-home aliasing: Enabled


R1#show l2vpn evpn evi detail
EVPN instance:       5 (VLAN Based)
  RD:                1.1.1.1:5 (auto)
  Import-RTs:        65010:5
  Export-RTs:        65010:5
  Per-EVI Label:     none
  State:             Established
  Replication Type:  Ingress (global)
  Encapsulation:     mpls
  Bridge Domain:     10
    Ethernet-Tag:    0
    BUM Label:       100
    Per-BD Label:    101
    State:           Established
    Access If:
    Pseudoports:
      Port-channel1 service instance 15 (DF state: forwarding)             « PE R1 elected as Designated Forwarder
        Routes: 0 MAC, 0 MAC/IP
    Peers:
      2.2.2.2
        Routes: 0 MAC, 0 MAC/IP, 1 IMET, 1 EAD
      6.6.6.6
        Routes: 0 MAC, 0 MAC/IP, 1 IMET, 0 EAD


R2#show l2vpn evpn evi detail
EVPN instance:       5 (VLAN Based)
  RD:                2.2.2.2:5 (auto)
  Import-RTs:        65010:5
  Export-RTs:        65010:5
  Per-EVI Label:     none
  State:             Established
  Replication Type:  Ingress (global)
  Encapsulation:     mpls
  Bridge Domain:     10
    Ethernet-Tag:    0
    BUM Label:       208
    Per-BD Label:    209
    State:           Established
    Access If:
    Pseudoports:
      Port-channel1 service instance 15 (DF state: PE-to-CE BUM blocked)        « Split-horizon filtering loop avoidance
        Routes: 0 MAC, 0 MAC/IP
    Peers:
      1.1.1.1
        Routes: 0 MAC, 0 MAC/IP, 1 IMET, 1 EAD
      6.6.6.6
        Routes: 0 MAC, 0 MAC/IP, 1 IMET, 0 EAD


R1#show l2vpn evpn ethernet-segment
ESI                      Port       Redundency Mode DF Time SH Label
------------------------ ---------- --------------- ------- --------
0300.0000.00CA.FE00.0001 Po1        all-active      3       16                  « All-active multihoming is configured


R1#show l2vpn evpn peers

EVI    BD    Peer-IP                   Num routes UP time
------ ----- ------------------------  ---------- --------
Global N/A   2.2.2.2                   2          02:25:54
5      10    2.2.2.2                   2          02:25:55                 « EVI instance number 5
5      10    6.6.6.6                   3          02:25:57


R1#show bridge-domain 10
Bridge-domain 10 (2 ports in all)
State: UP                    Mac learning: Enabled             « MAC learning enabled on PE
Aging-Timer: 300 second(s)
Maximum address limit: 65536
    Port-channel1 service instance 15
    EVPN Instance 5
   AED MAC address    Policy  Tag       Age  Pseudoport
   -   001E.BD2E.DAC9 forward static_a  0    Port-channel1.EFP15
   -   5254.000D.020E forward static_r  0    OCE_PTR:0xe8db5840
   -   5254.0018.A67B forward static_r  0    OCE_PTR:0xe8db5840